

Vous avez une actualité à partager avec le secteur événementiel ?
Envoyez un communiqué de presse ou une information et touchez des milliers de professionnels de l'événementiel.
Nous contacter→Plus dans Cybersecurity, Cryptography & Digital Trust

Dark Reading
Alleged KillSec Ransomware Mastermind a 16-Year-Old
The Hacker News
Police Arrest 16-Year-Old Suspected of Running KillSec, Seize Ransomware Leak Site and Servers
The Hacker News
Google Rolls Out Gemini 4 Argon to Trusted Cyber Defenders, Plans Guardrail-Free Version

Dark Reading
Malicious Custom GPTs Turn ChatGPT Into RAT Delivery Lure

Dark Reading
As AI Reshapes the SOC Career Ladder, Satisfaction Rises for 91%, but Entry Gets Harder for Nearly Half

Dark Reading
Russia's Star Blizzard Ditches ClickFix to Widen Phishing Net
Articles connexes
 Advanced manufacturing and industrial AI
Unlocking Deep Tech: The Science Is Ready. The Race Is to Build It.
Why refining, energy and "boring" supply chains may beat the headline technologies. Unlocking Deep Tech: what it is, who leads, what 2030 looks like across seven regions and where the growth opportunities are.
22 min read Workforce transformation and the future of skills
The Middle East’s Future Economy: The Industries, Partnerships, and Workforce Roadmaps That Could Define the Next Era
The Middle East is using partnerships with China and India to build future industries in AI, clean energy, logistics, manufacturing, health, food security, and tourism. Success will depend on workforce development, sovereignty, investment quality, and turning ambition into lasting capability.
13 min read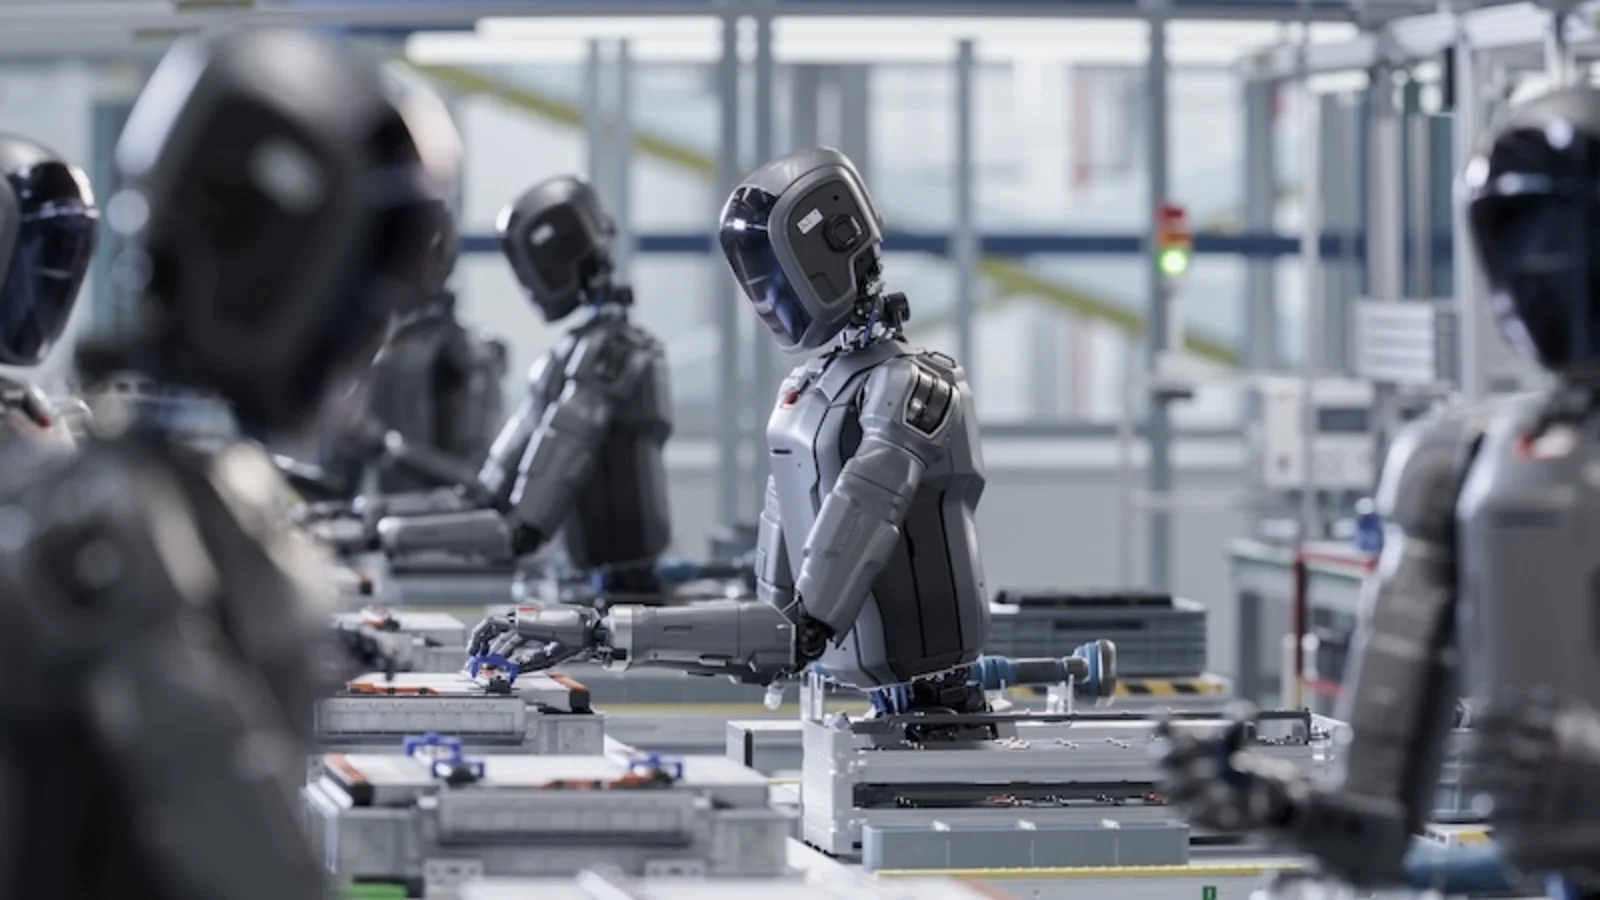 Advanced manufacturing and industrial AI
Dark Factories and Robotics
How China turned automated factories and humanoid robots into a single industrial machine — and where the opportunities are opening.
9 min read