
Got news to share with the events industry?
Submit a press release or story tip and reach thousands of event professionals.
Get in touch→More in Cybersecurity, Cryptography & Digital Trust
Dark Reading
ASOS Breach Reveals the Risks in Customer-Facing SaaS
The Hacker News
P7 DarkSword iOS Exploit Kit Adds Crypto Wallet Data Theft and Remote Commands
Dark Reading
What We Missed: FBI Strikes Back at ShinyHunters
The Hacker News
Anthropic Cuts Live Internet Access for Internal AI Tests After Claude Exploits Injection Flaws
The Hacker News
Bring Your Own Agent: Your Employees' Assistants Are Already Logged In
Dark Reading
Security Threats Don't Stop at the Office: Why Executives' Families Need Training, Too
Related Insights
 Clean energy and grid modernization
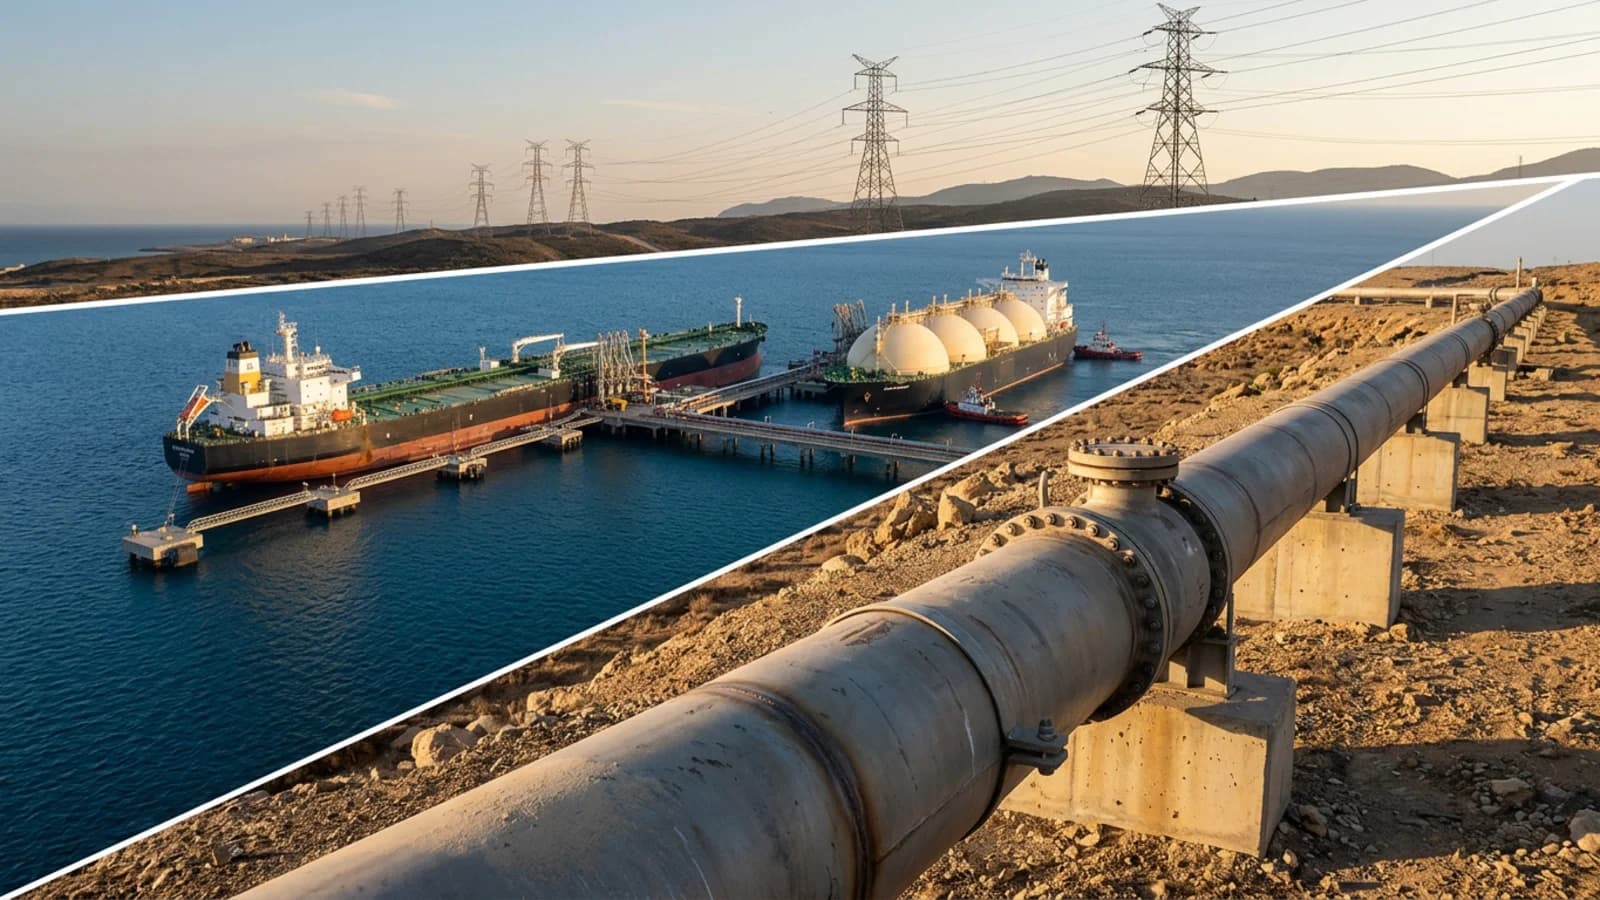
The Hidden Global Highways of Energy
How Oil, Gas and Power Move Around the World, and Who Keeps Them Flowing
23 min read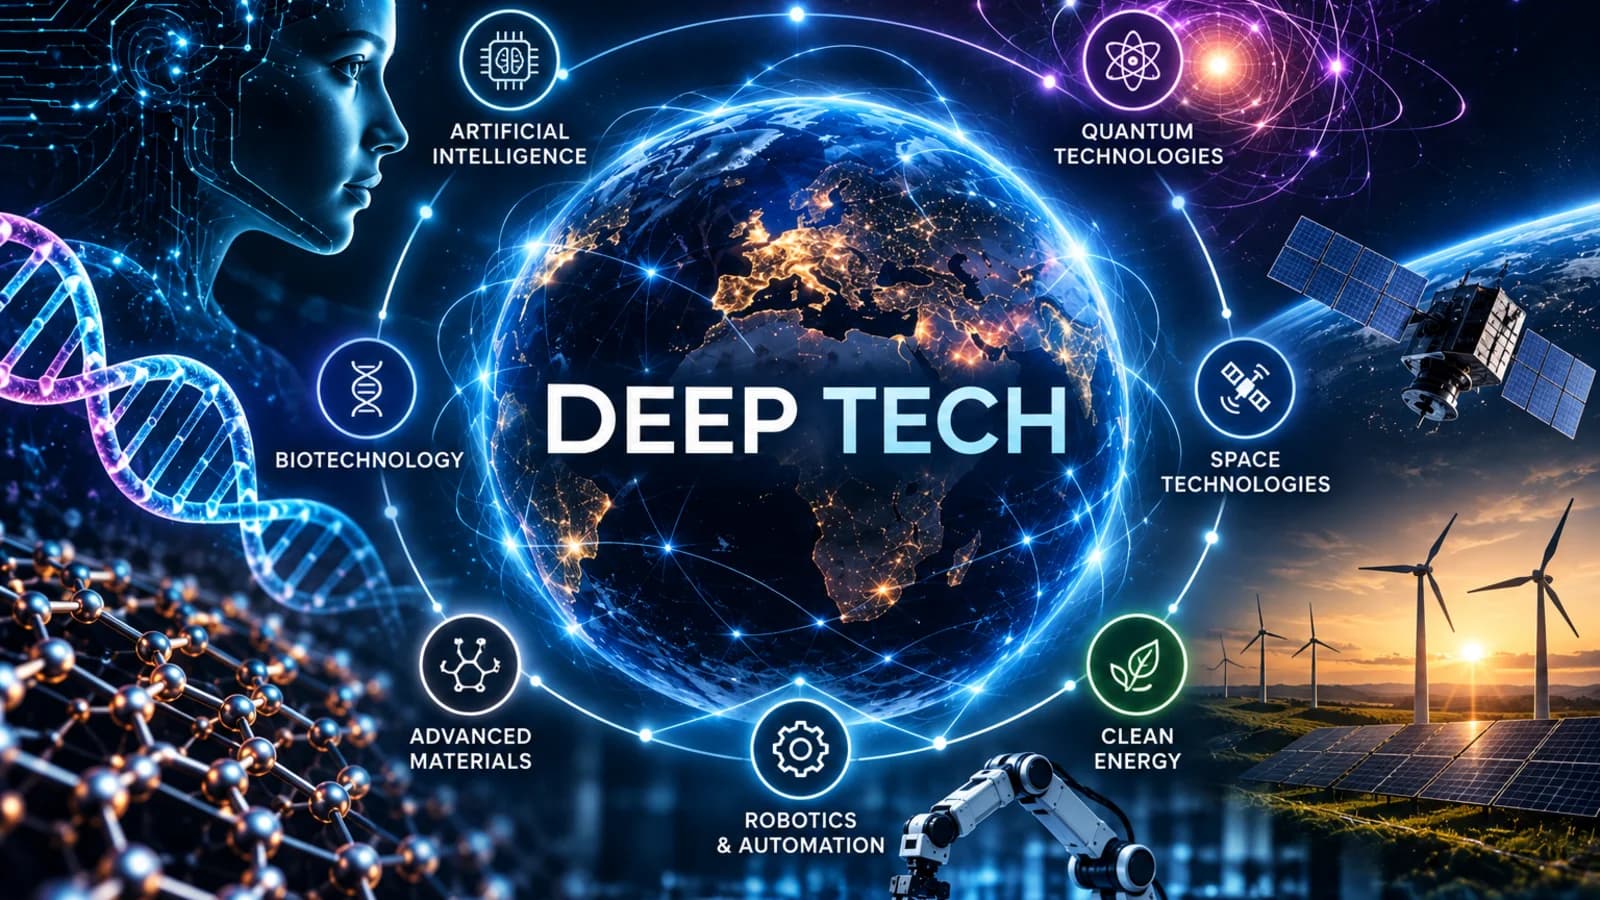 Advanced manufacturing and industrial AI
Unlocking Deep Tech: The Science Is Ready. The Race Is to Build It.
Why refining, energy and "boring" supply chains may beat the headline technologies. Unlocking Deep Tech: what it is, who leads, what 2030 looks like across seven regions and where the growth opportunities are.
22 min read Workforce transformation and the future of skills
Industries, Partnerships, and Workforce Roadmaps That Could Define the Next Era
The Middle East is using partnerships with China and India to build future industries in AI, clean energy, logistics, manufacturing, health, food security, and tourism. Success will depend on workforce development, sovereignty, investment quality, and turning ambition into lasting capability.
15 min read