
Got news to share with the events industry?
Submit a press release or story tip and reach thousands of event professionals.
Get in touch→More in Cybersecurity, Cryptography & Digital Trust
Dark Reading
Anthropic Gives Vetted Defenders Fewer Claude Guardrails
Dark Reading
Critical Healthcare Systems Aren't Quantum-Ready
Dark Reading
Google's PageBreak AI Agent Finds 500 Flaws in Its Web Apps
Dark Reading
Citizen Lab Slams Trump Administration, 'Techno-Fascist' Executives
The Hacker News
What Is Agentic Pentesting? What It Proves, and Where It Stops.
The Hacker News
Linux Backdoors Impersonate Email Security Tools to Evade Detection in Korea and Taiwan
Related Insights
 Advanced manufacturing and industrial AI
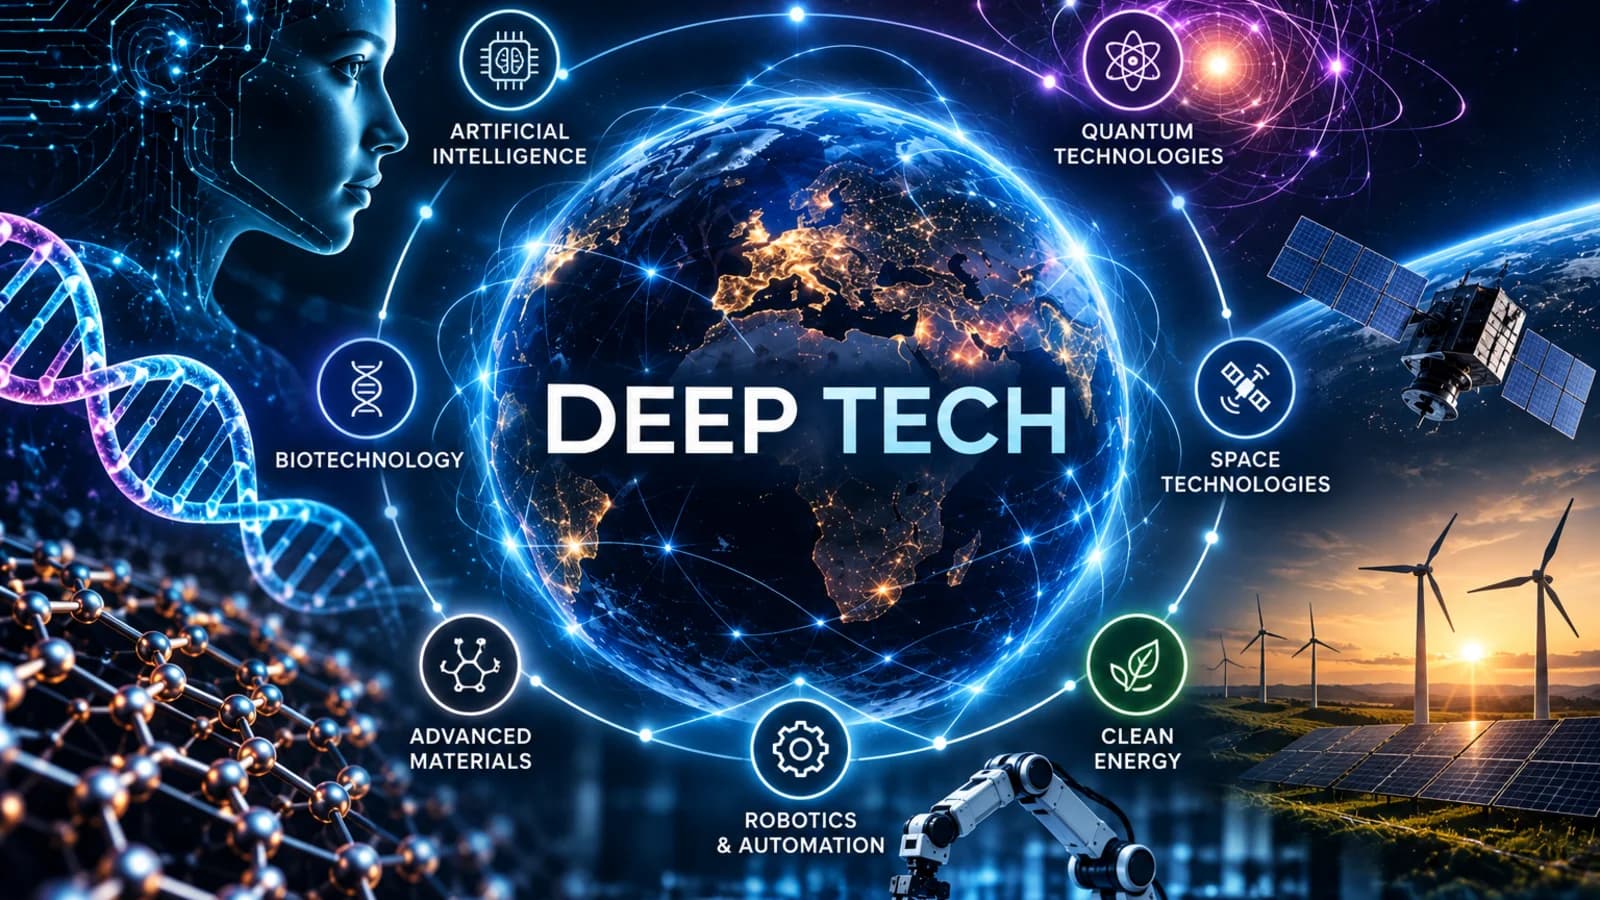
Unlocking Deep Tech: The Science Is Ready. The Race Is to Build It.
Why refining, energy and "boring" supply chains may beat the headline technologies. Unlocking Deep Tech: what it is, who leads, what 2030 looks like across seven regions and where the growth opportunities are.
22 min read Workforce transformation and the future of skills
The Middle East’s Future Economy: The Industries, Partnerships, and Workforce Roadmaps That Could Define the Next Era
The Middle East is using partnerships with China and India to build future industries in AI, clean energy, logistics, manufacturing, health, food security, and tourism. Success will depend on workforce development, sovereignty, investment quality, and turning ambition into lasting capability.
13 min read Advanced manufacturing and industrial AI
Dark Factories and Robotics
How China turned automated factories and humanoid robots into a single industrial machine — and where the opportunities are opening.
9 min read