
Got news to share with the events industry?
Submit a press release or story tip and reach thousands of event professionals.
Get in touch→More in Cybersecurity, Cryptography & Digital Trust
The Hacker News
uCreator Android Spyware Can Steal Telegram 2FA Passwords and Clone WeChat Accounts
The Hacker News
PHP Issues Second Windows Security Update in Five Days to Fix Brotli Code Execution Flaw
The Hacker News
CISA Confirms Active Exploitation of Two PHP2Shell Flaws Enabling Remote Code Execution
The Hacker News
Two Critical Wasmtime Flaws Could Let Malicious WebAssembly Modules Escape Sandboxes
Tradepass
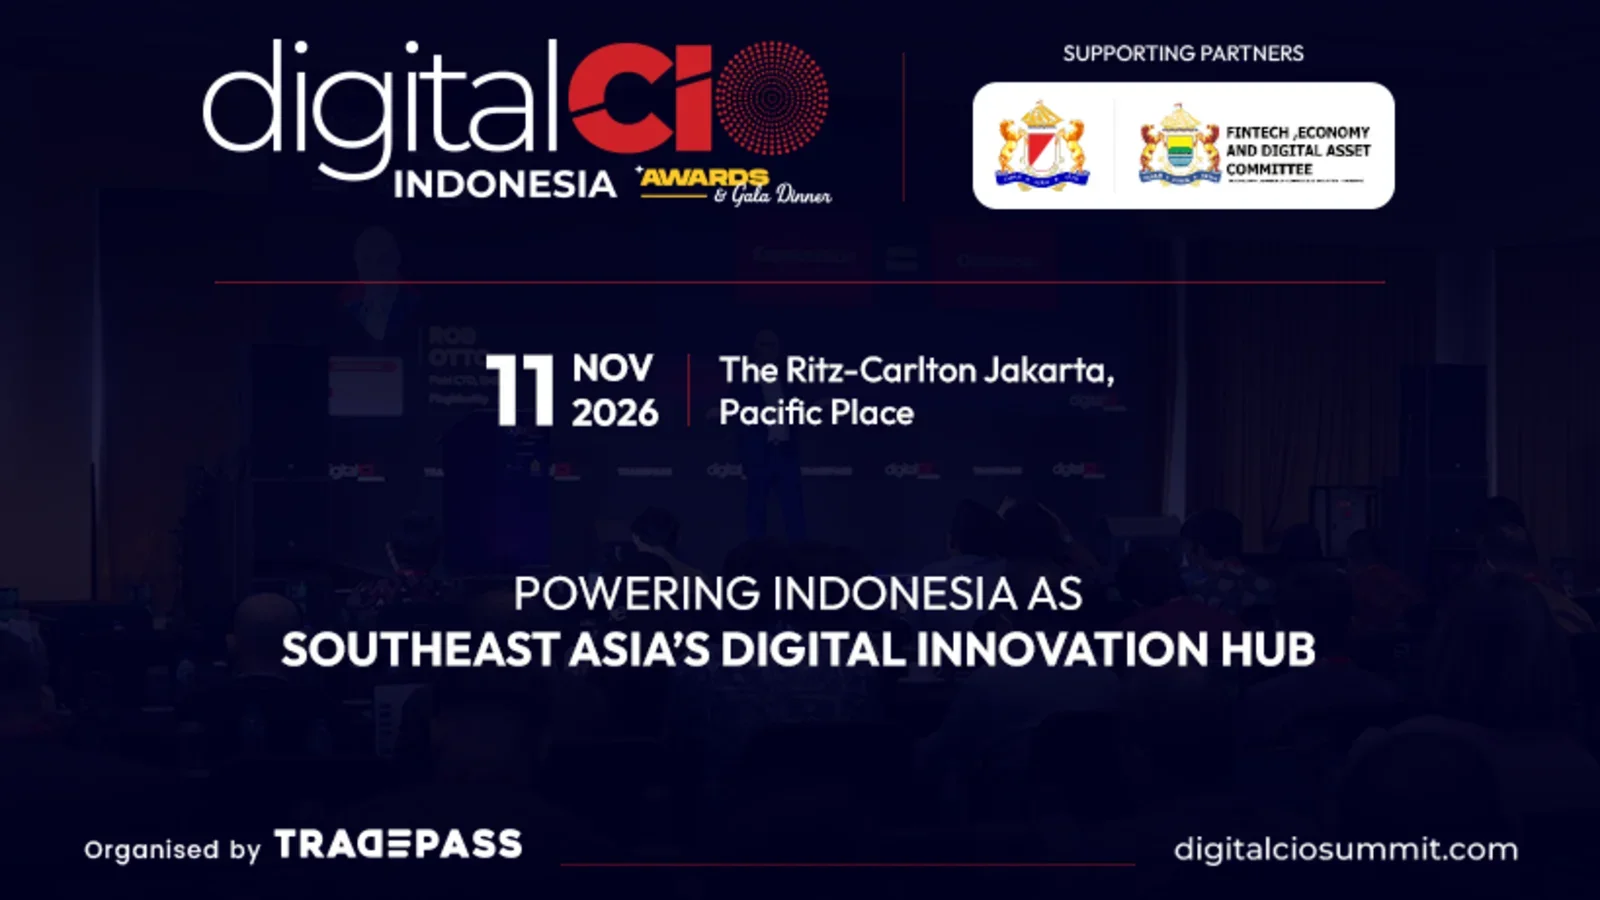
Indonesia’s Digital Future Moves into the Spotlight as digitalCIO Indonesia 2026 Draws Strong Institutional Backing and Cross-Industry Participation
The Hacker News
Brotli Decoder Flaw Behind Node.js RCE Also Affects Bun, Python and Other Widely Used Software
Related Insights
 Supply chain intelligence
The Floating Economy: How Tankers and Cargo Ships Quietly Run the World
12.7 billion tonnes of goods cross the oceans a year, yet most people never see the ships. Discover how the tanker and cargo shipping business really works, who owns, builds and crews the fleet, why one strait can shake oil prices, and where the next careers and opportunities are.
24 min read Smart agriculture and food technology
Food = Power
How China Plans to Never Run Out of Food and What the Rest of the World Can Learn
21 min read Clean energy and grid modernization
The Hidden Global Highways of Energy
How Oil, Gas and Power Move Around the World, and Who Keeps Them Flowing
23 min read