
Got news to share with the events industry?
Submit a press release or story tip and reach thousands of event professionals.
Get in touch→More in Cybersecurity, Cryptography & Digital Trust
Dark Reading
N-able Takes N-central Platform Offline After Discovery of 33 Flaws
Dark Reading
Chinese AI Project Scouts Spies in Taiwan Chip Industry
The Hacker News
eMudhra Revokes 8 More CAs It Previously Declared Unaffected by Key Compromise
The Hacker News
AntiFox AI Pentesting Platform Linked to Attacks That Accessed AWS Production Secrets
Dark Reading
Artex: The AI Pen-Test Tool Hackers Turned Into a Weapon
Dark Reading
F-Secure Identifies 26 Ways AI Can Harm Consumers, and Where to Stop Them
Related Insights
 Workforce transformation and the future of skills
The Time Paradox: Why Being Busy Doesn't Mean You're Moving Forward - The Foundations of Lasting Success Week 1
Busy calendars can hide stalled progress. Reclaim your attention, protect priorities, and make time for future growth.
13 min read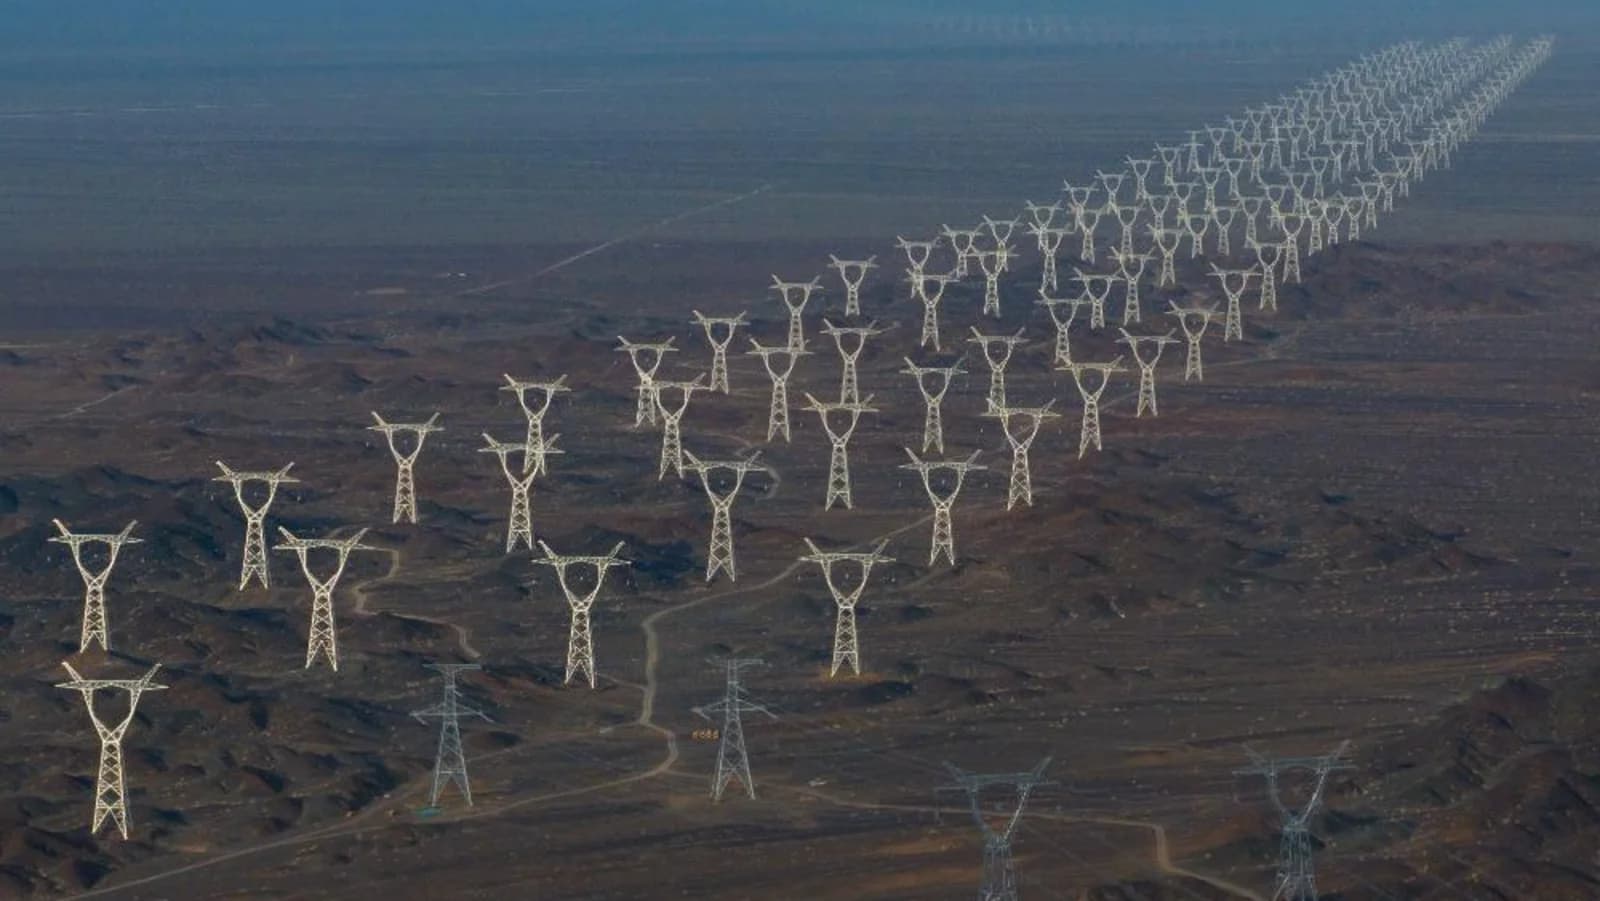 Clean energy and grid modernization
The Grid Gamble: How Electricity Could Decide the Next Industrial Superpower
China is building more than power stations and transmission lines. It is developing an electricity system designed to support AI, advanced manufacturing, electric vehicles, renewable energy, and future industries. The ambition is enormous, but so are the engineering and economic challenges.
15 min read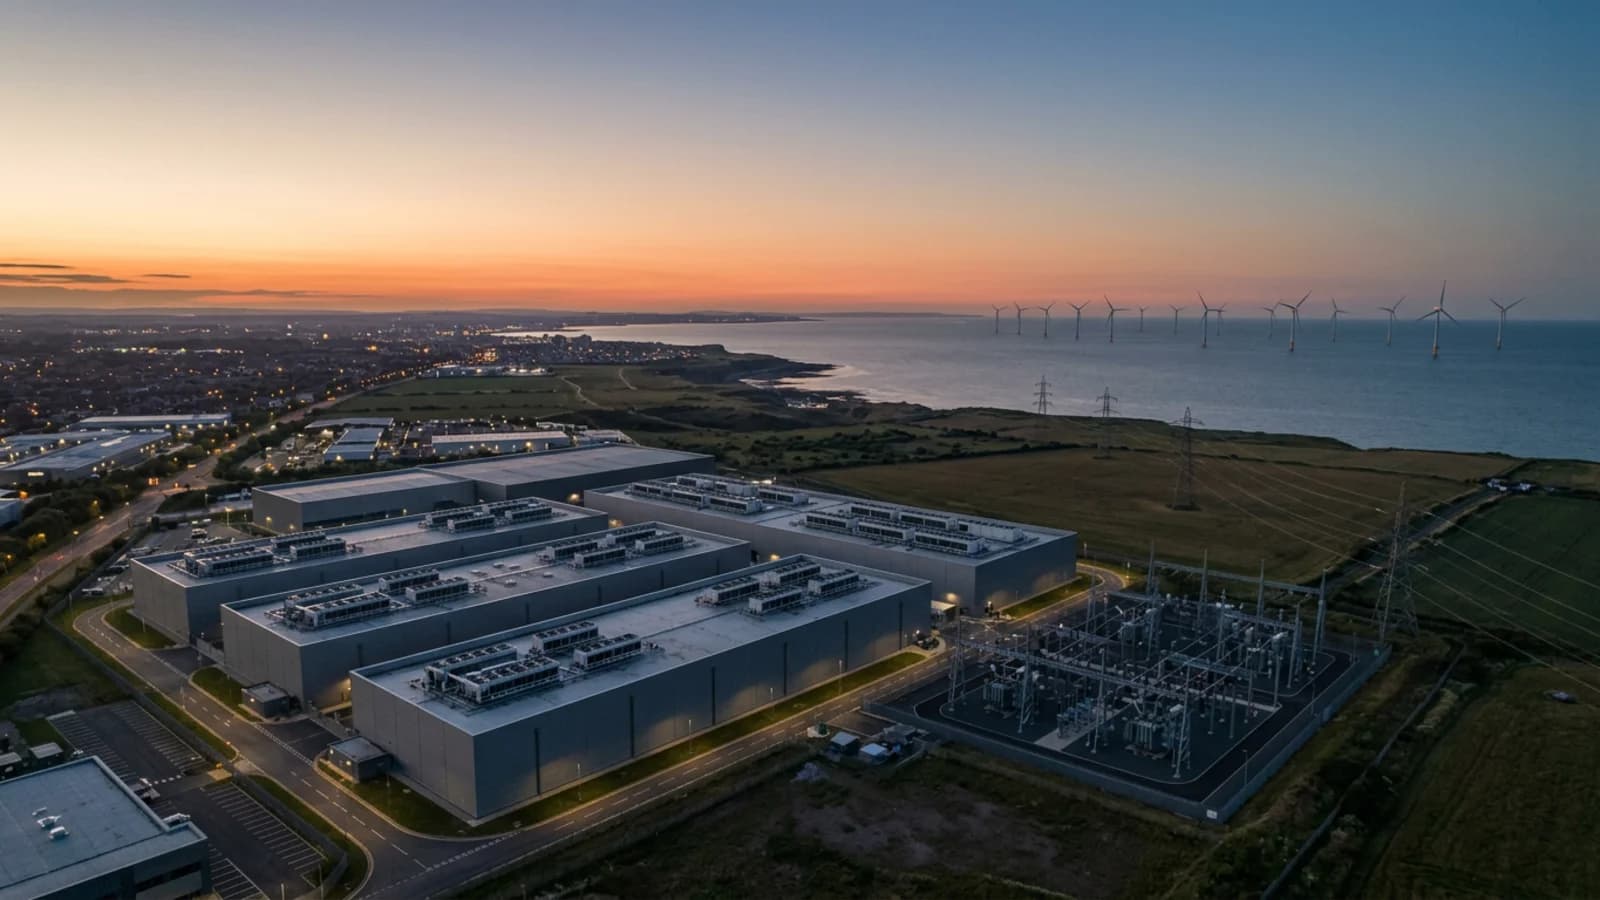 AI infrastructure
Inside the Cloud, Part 2: The AI Gold Rush Has a Plumbing Problem — and That's Just the Beginning
The expansion of artificial intelligence is creating a much larger industrial economy than most people realize. Behind the computers are energy producers, mining companies, engineers, skilled tradespeople, security specialists, and investors.
20 min read