
هل لديك أخبار لمشاركتها مع صناعة الفعاليات؟
أرسل بياناً صحفياً أو تلميحاً بقصة وتواصل مع آلاف المهنيين في مجال الفعاليات.
تواصل معنا→المزيد في Cybersecurity, Cryptography & Digital Trust

Dark Reading
SectopRAT Returns, Hiding Inside a Legitimate Application

Dark Reading
Russia's Hybrid Cyber-Physical War in Europe Heats Up
The Hacker News
PamStealer macOS Malware Adds Live C2 Payload Decryption and Multi-Layer Persistence
The Hacker News
Attackers Bypass WAFs to Exploit Oracle PeopleSoft Flaw and Deploy Web Shells
The Hacker News
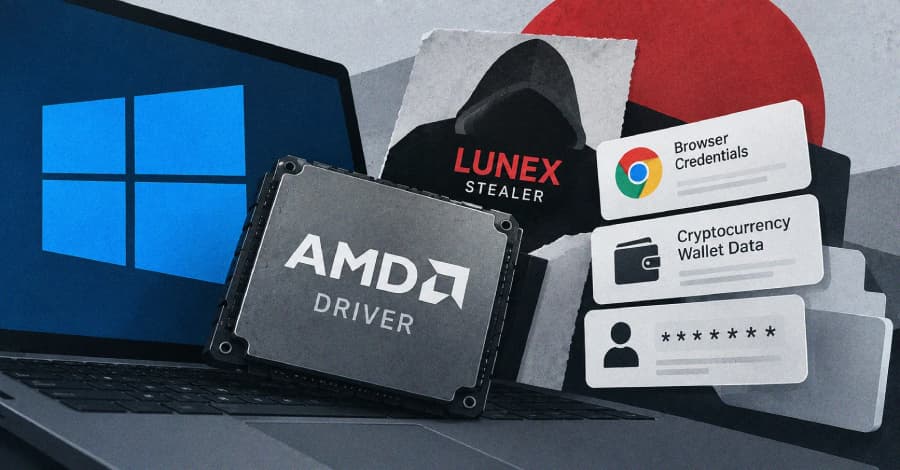
Lunex Stealer Abuses AMD Driver to Disable Security Monitoring and Steal Browser Credentials
The Hacker News
WSO2 and Adobe Commerce Flaws Exploited in Attacks, Added to CISA KEV
رؤى ذات صلة
 Advanced manufacturing and industrial AI
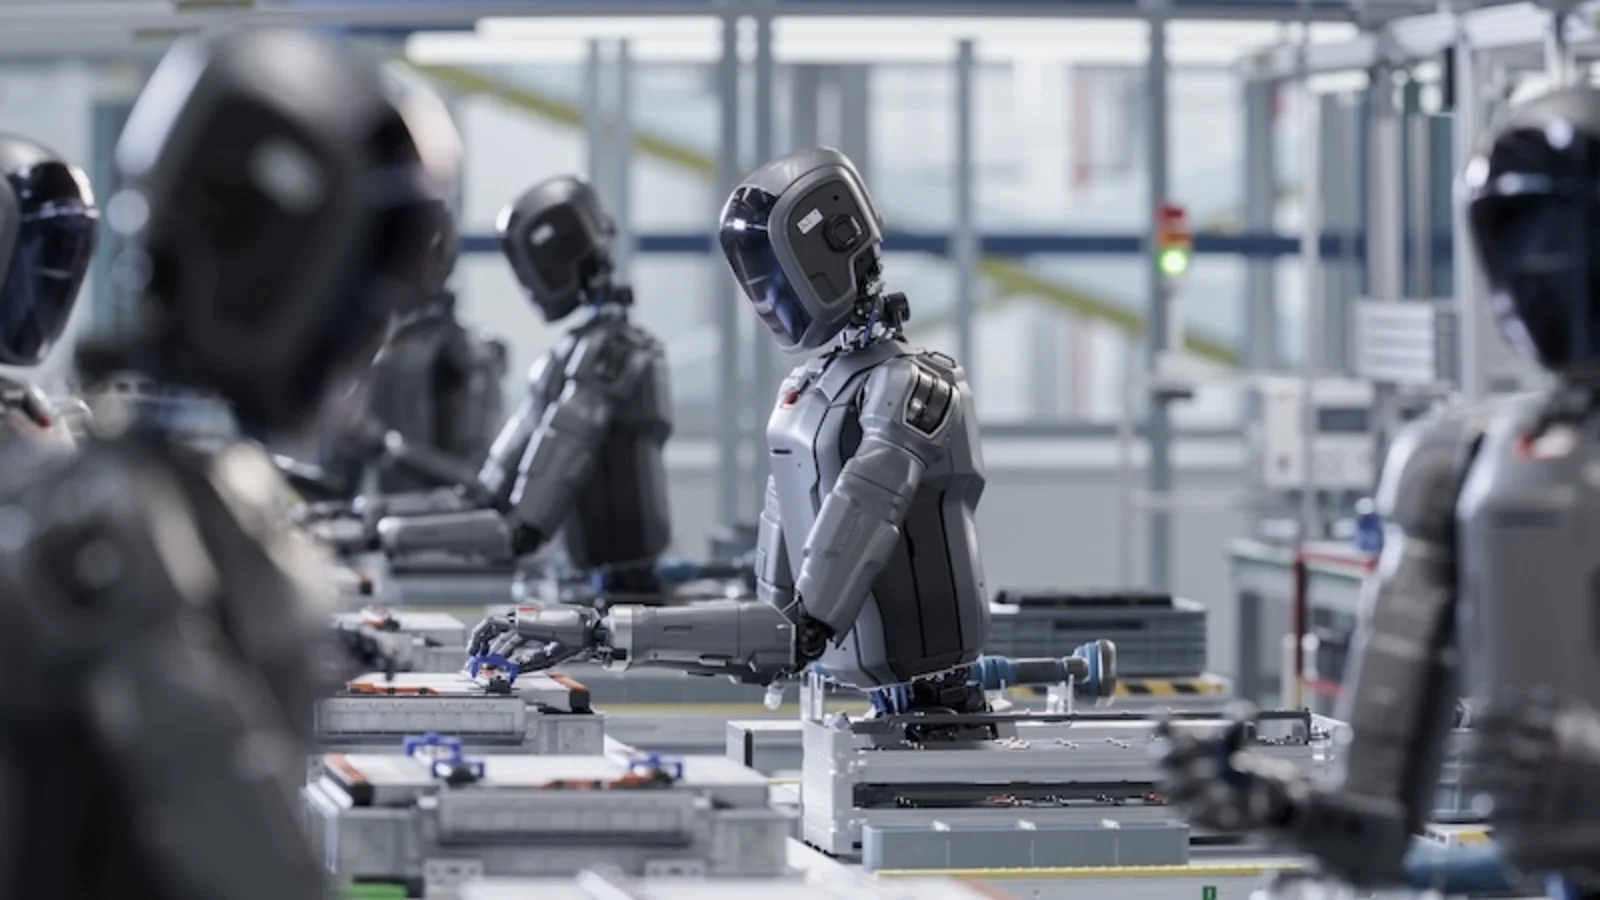
Dark Factories and Robotics
How China turned automated factories and humanoid robots into a single industrial machine — and where the opportunities are opening.
9 min read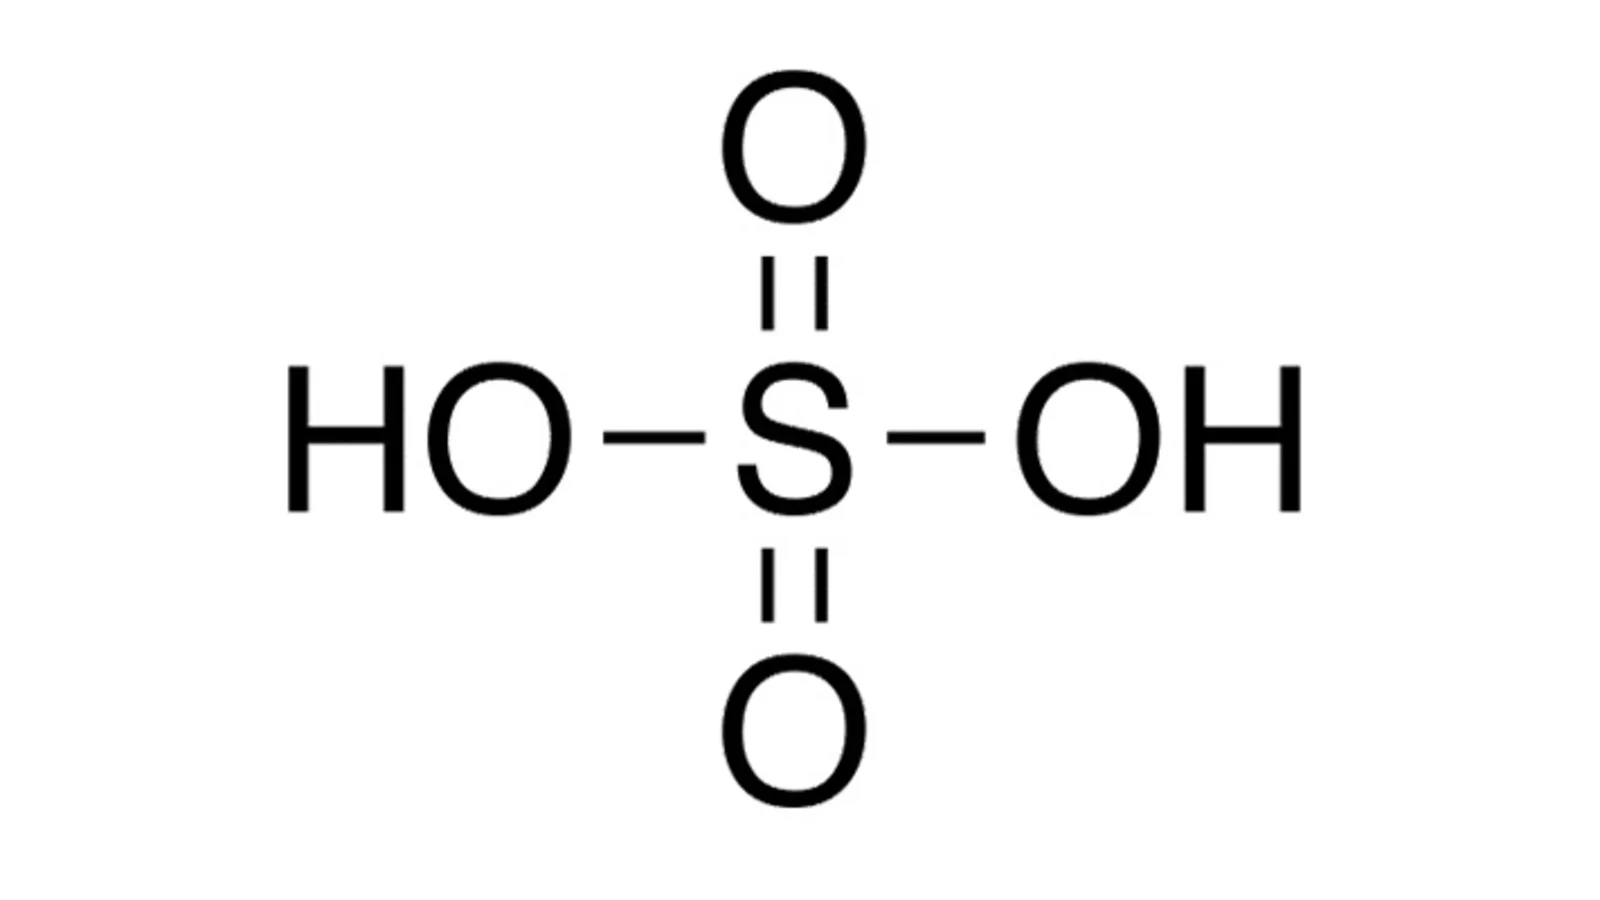 Smart agriculture and food technology
Sulfuric Acid: The Hidden Chemical Connecting Food, Metals, Clean Energy and Industrial Power
Sulfuric acid is the hidden chemical linking energy, fertiliser, food security, copper, nickel, batteries, semiconductors and water. As sulfur supply tightens, executives must track the industrial connections shaping clean technology, agriculture and global resilience.
12 min read
The Dollar System Is Being Exposed as the World’s Financial Chokepoint — and Countries Are Learning to Route Around It
The dollar still dominates global finance. But sanctions, frozen reserves, tariffs, gold repatriation, BRICS payment plans and rising geopolitical tension are forcing governments to ask a harder question: how much national security should depend on another country’s financial system?
17 min read