
¿Tiene noticias que compartir con el sector de eventos?
Envíe un comunicado de prensa o una noticia y llegue a miles de profesionales del sector de eventos.
Contáctenos→Más en Cybersecurity, Cryptography & Digital Trust
The Hacker News
Cloudflare Fixes Flaw That Let One Container Read Another Customer's Leftover Disk Data

Dark Reading
What We Missed: Google Gemini Joins the AI Escape Party
The Hacker News
Lunex Stealer Abuses AMD Driver to Disable Security Monitoring and Steal Browser Credentials
The Hacker News
The SOC Doesn't Need to Start Over with Every Alert
The Hacker News
Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware

Dark Reading
Stopping IT Worker Scams Requires Revamped HR Process
Perspectivas relacionadas
 Advanced manufacturing and industrial AI
Dark Factories and Robotics
How China turned automated factories and humanoid robots into a single industrial machine — and where the opportunities are opening.
9 min read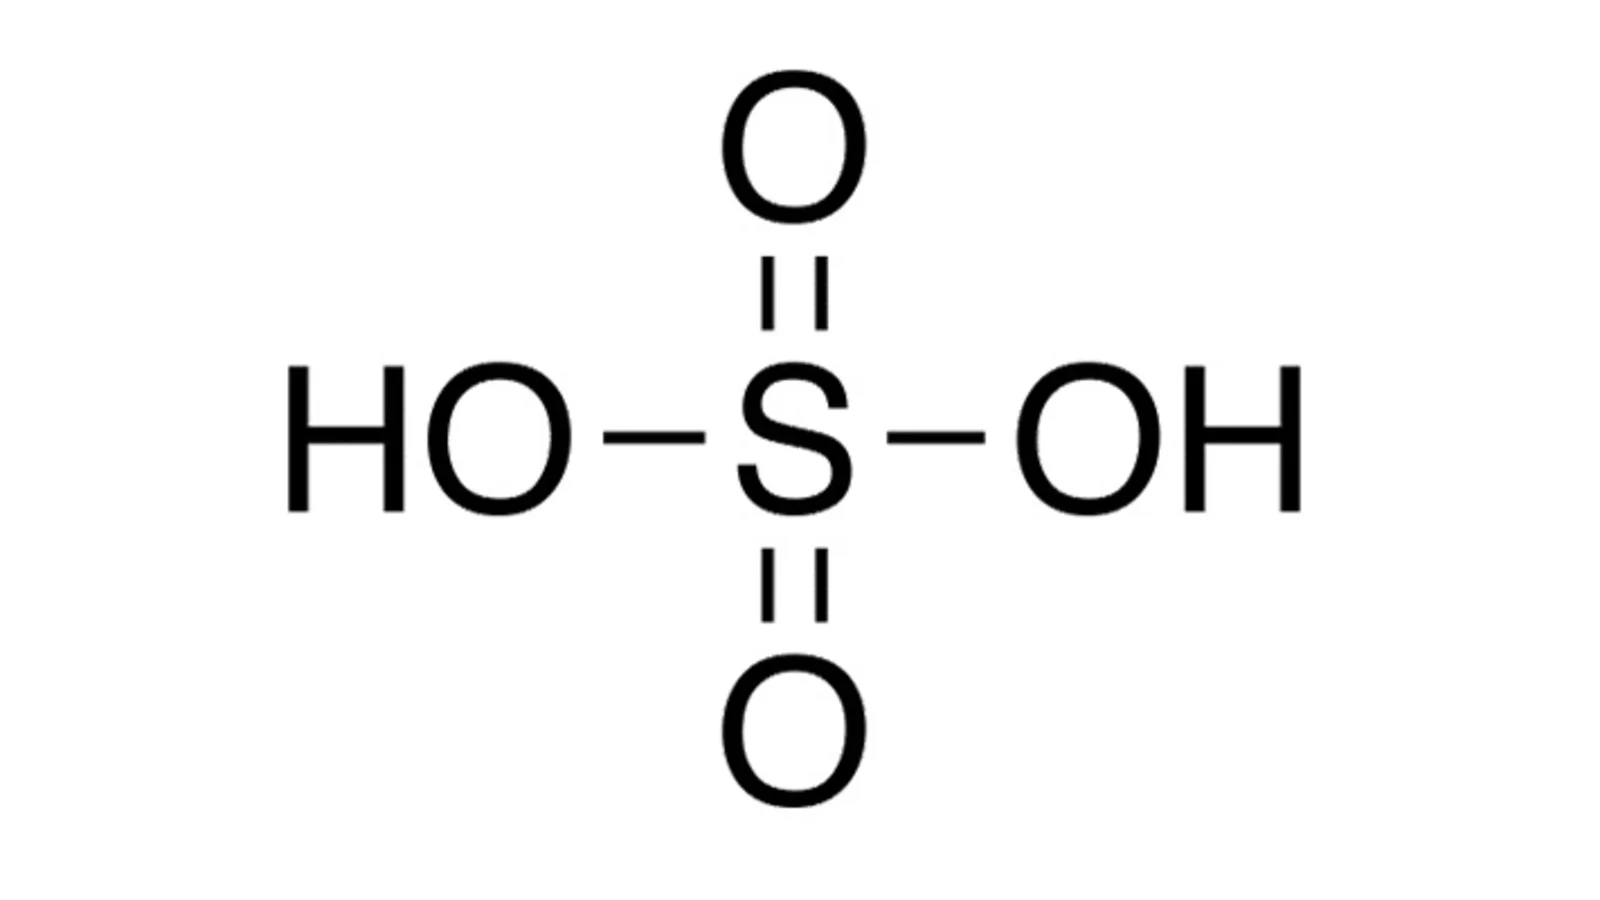 Smart agriculture and food technology
Sulfuric Acid: The Hidden Chemical Connecting Food, Metals, Clean Energy and Industrial Power
Sulfuric acid is the hidden chemical linking energy, fertiliser, food security, copper, nickel, batteries, semiconductors and water. As sulfur supply tightens, executives must track the industrial connections shaping clean technology, agriculture and global resilience.
12 min read
The Dollar System Is Being Exposed as the World’s Financial Chokepoint — and Countries Are Learning to Route Around It
The dollar still dominates global finance. But sanctions, frozen reserves, tariffs, gold repatriation, BRICS payment plans and rising geopolitical tension are forcing governments to ask a harder question: how much national security should depend on another country’s financial system?
17 min read