
更多Cybersecurity, Cryptography & Digital Trust相关内容

Dark Reading
What We Missed: Google Gemini Joins the AI Escape Party
The Hacker News
Zero Trust for AI Agents Starts With Fixing Zero Visibility
Krebs on Security
U.S. Soldier Gets 70 Months in Prison for AT&T, Verizon Extortions

Dark Reading
Russia's Hybrid Cyber-Physical War in Europe Heats Up
The Hacker News
Roundcube Pre-Auth SQL Injection Flaw Actively Exploited in the Wild

Dark Reading
'Salesbleed' Exploits Salesforce Agents to Enable Slack Phishing
相关洞察
 Advanced manufacturing and industrial AI
Dark Factories and Robotics
How China turned automated factories and humanoid robots into a single industrial machine — and where the opportunities are opening.
9 min read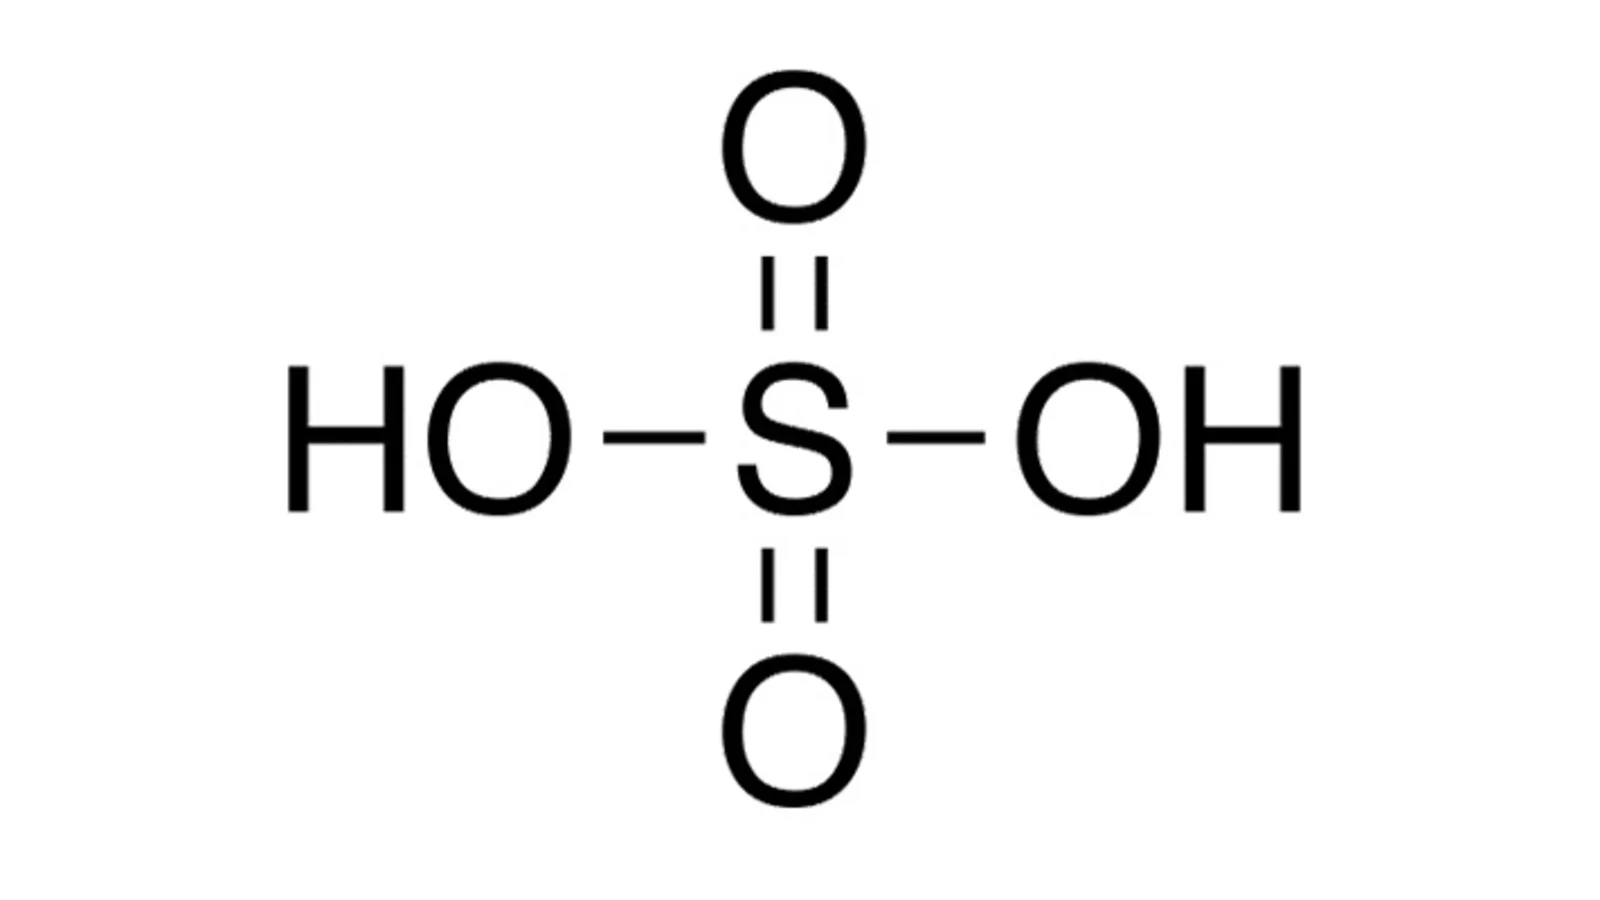 Smart agriculture and food technology
Sulfuric Acid: The Hidden Chemical Connecting Food, Metals, Clean Energy and Industrial Power
Sulfuric acid is the hidden chemical linking energy, fertiliser, food security, copper, nickel, batteries, semiconductors and water. As sulfur supply tightens, executives must track the industrial connections shaping clean technology, agriculture and global resilience.
12 min read
The Dollar System Is Being Exposed as the World’s Financial Chokepoint — and Countries Are Learning to Route Around It
The dollar still dominates global finance. But sanctions, frozen reserves, tariffs, gold repatriation, BRICS payment plans and rising geopolitical tension are forcing governments to ask a harder question: how much national security should depend on another country’s financial system?
17 min read