
Got news to share with the events industry?
Submit a press release or story tip and reach thousands of event professionals.
Get in touch→More in Cybersecurity, Cryptography & Digital Trust
The Hacker News
⚡ Weekly Recap: Helpdesk 0-Days, Rogue Certs, ShinyHunters Arrest, AI-Fooling Malware and More
Dark Reading
North Korea Phishes Ukrainians for War Intel
Dark Reading
Zero-Days Lurk in Microsoft's Overgrown October Patch Tuesday
Dark Reading
Prominent Ransomware Negotiator Faces Extortion Charges
The Hacker News
Docker Fixes Critical Two-Year-Old Hub Flaw That Let One User Push Images as Another
Dark Reading
Anthropic Finds Ingredients for Future AI Worms
Related Insights
 Smart agriculture and food technology
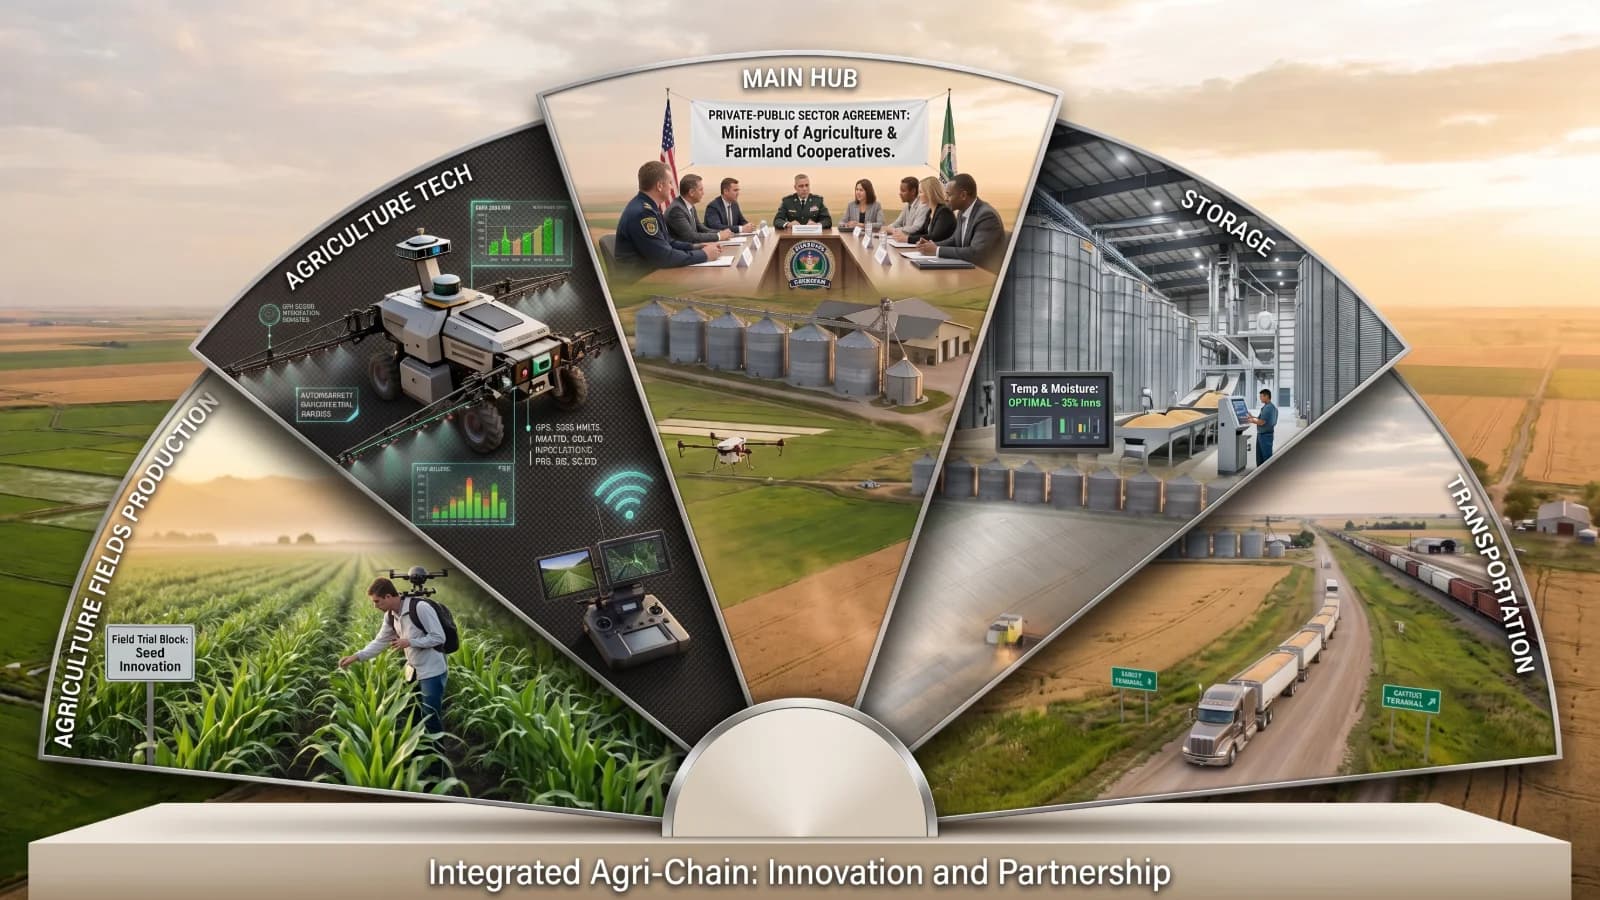
Food = Power
How China Plans to Never Run Out of Food and What the Rest of the World Can Learn
21 min read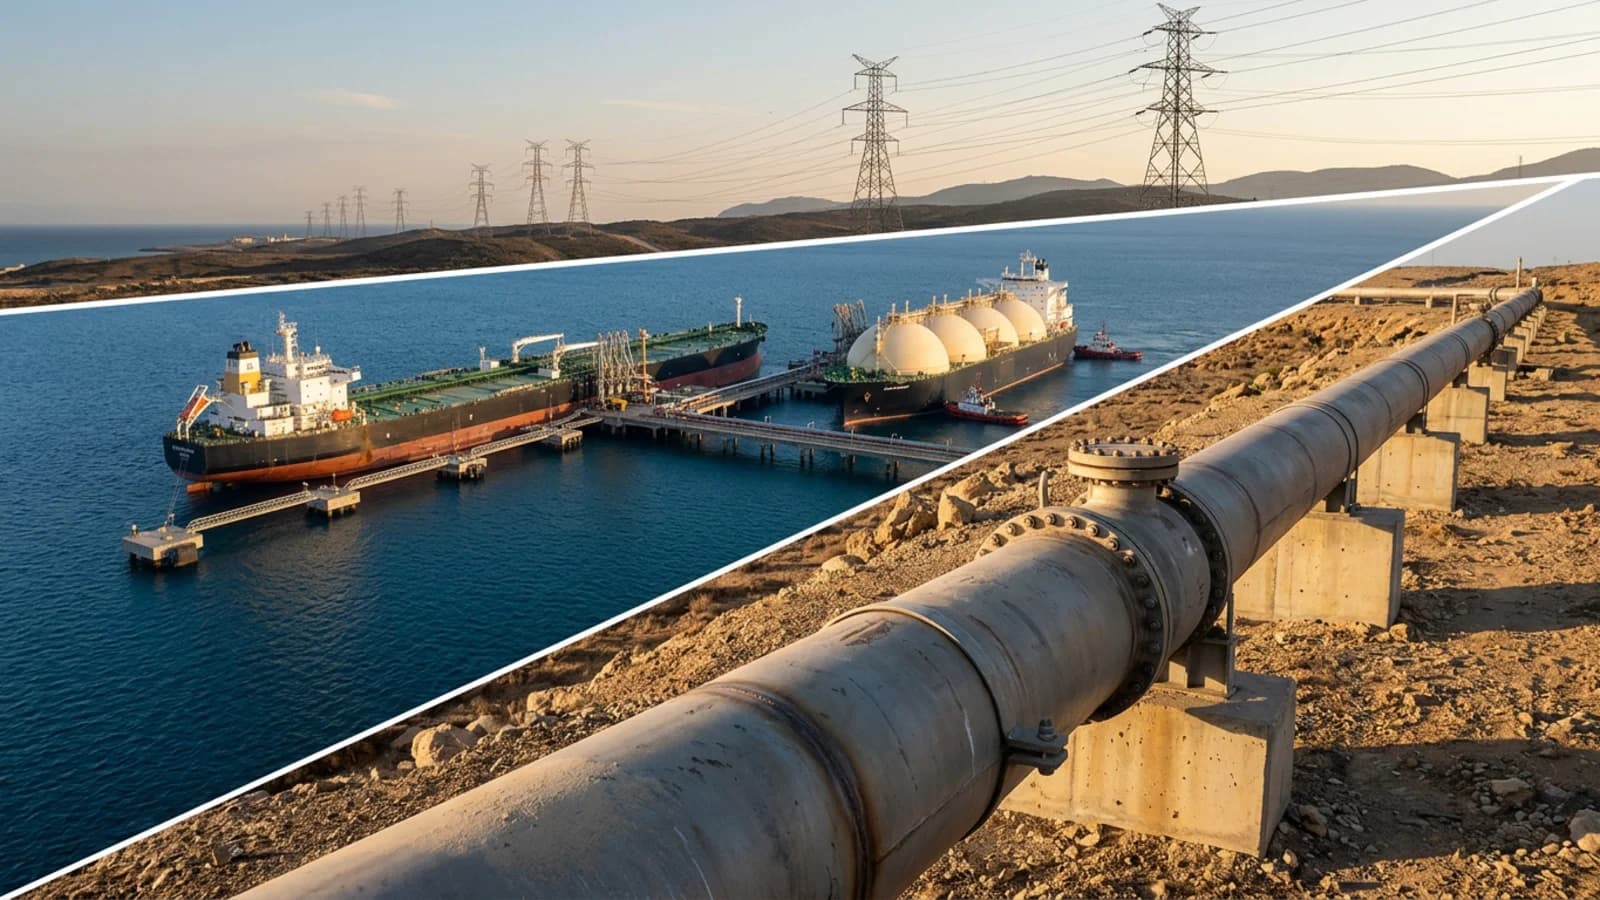 Clean energy and grid modernization
The Hidden Global Highways of Energy
How Oil, Gas and Power Move Around the World, and Who Keeps Them Flowing
23 min read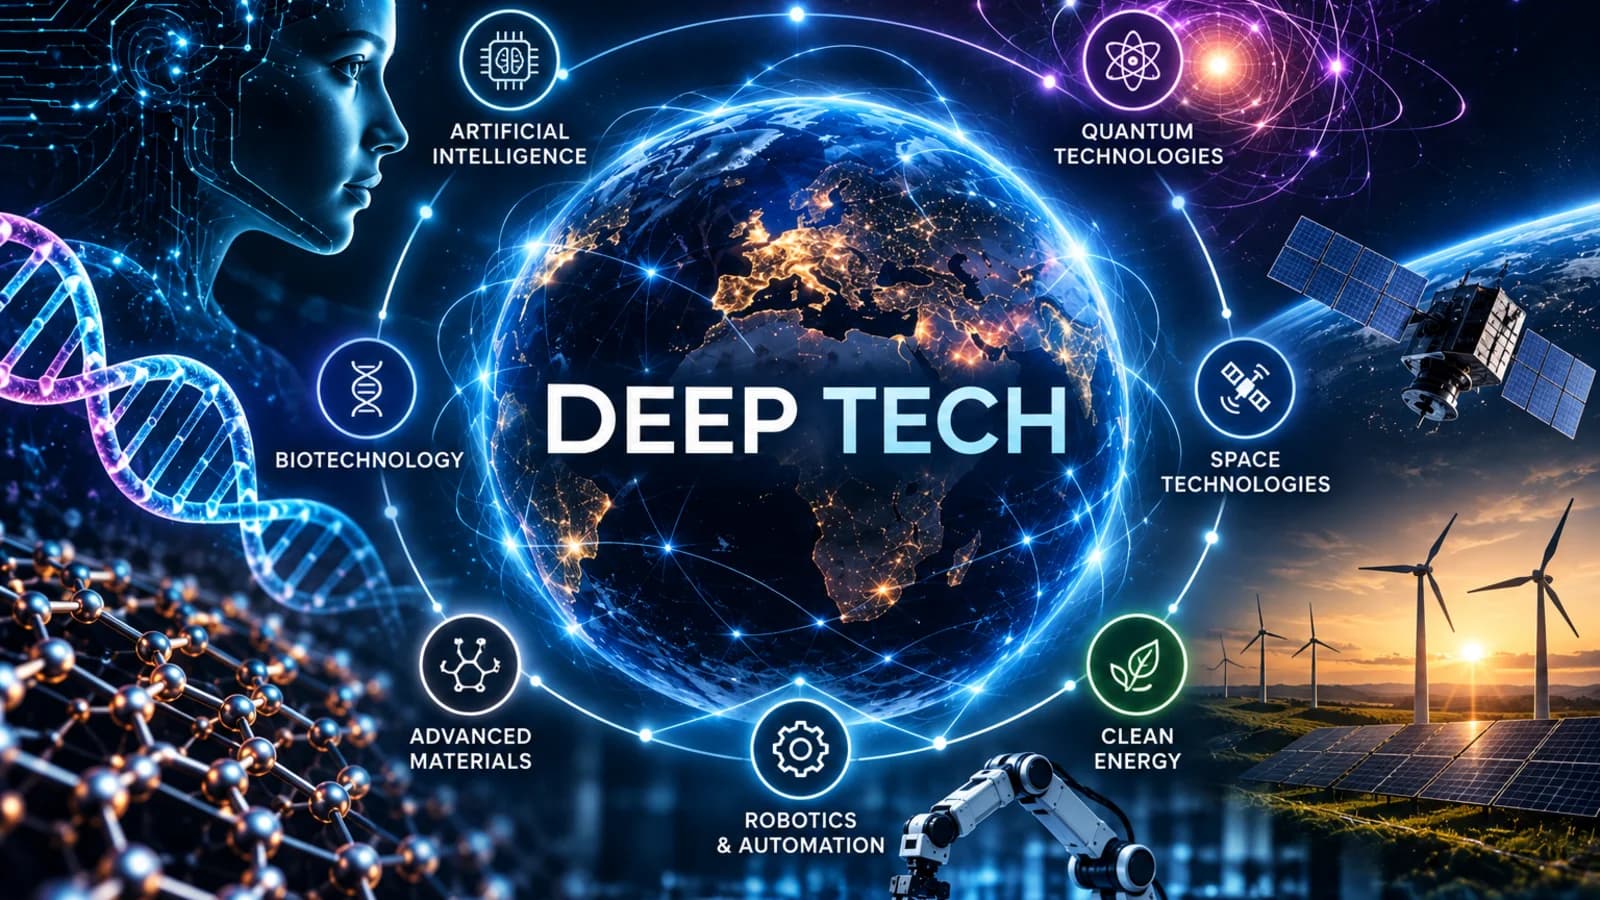 Advanced manufacturing and industrial AI
Unlocking Deep Tech: The Science Is Ready. The Race Is to Build It.
Why refining, energy and "boring" supply chains may beat the headline technologies. Unlocking Deep Tech: what it is, who leads, what 2030 looks like across seven regions and where the growth opportunities are.
22 min read