
Got news to share with the events industry?
Submit a press release or story tip and reach thousands of event professionals.
Get in touch→More in Cybersecurity, Cryptography & Digital Trust
Dark Reading
Why Europe's Freezer Hacks Spread So Far, So Fast
The Hacker News
Claude Code's “Don't Ask Again” File Exposes Passwords and Keys in 1,122 Public Copies on GitHub
Dark Reading
What We Missed: Knicks Phishing Test Goes Out of Bounds
Dark Reading
SecurityDataPipeline.com Launches as a New Educational Resource for the AI Era
Dark Reading
UK Wades Into Tech Sovereignty Amid AI Policy Changes
The Hacker News
OpenSSH Issues Emergency Fix for Flaw Letting Long Passwords Bypass SSH Auth on Alpine Linux
Related Insights
 Workforce transformation and the future of skills
The Time Paradox: Why Being Busy Doesn't Mean You're Moving Forward - The Foundations of Lasting Success Week 1
Busy calendars can hide stalled progress. Reclaim your attention, protect priorities, and make time for future growth.
13 min read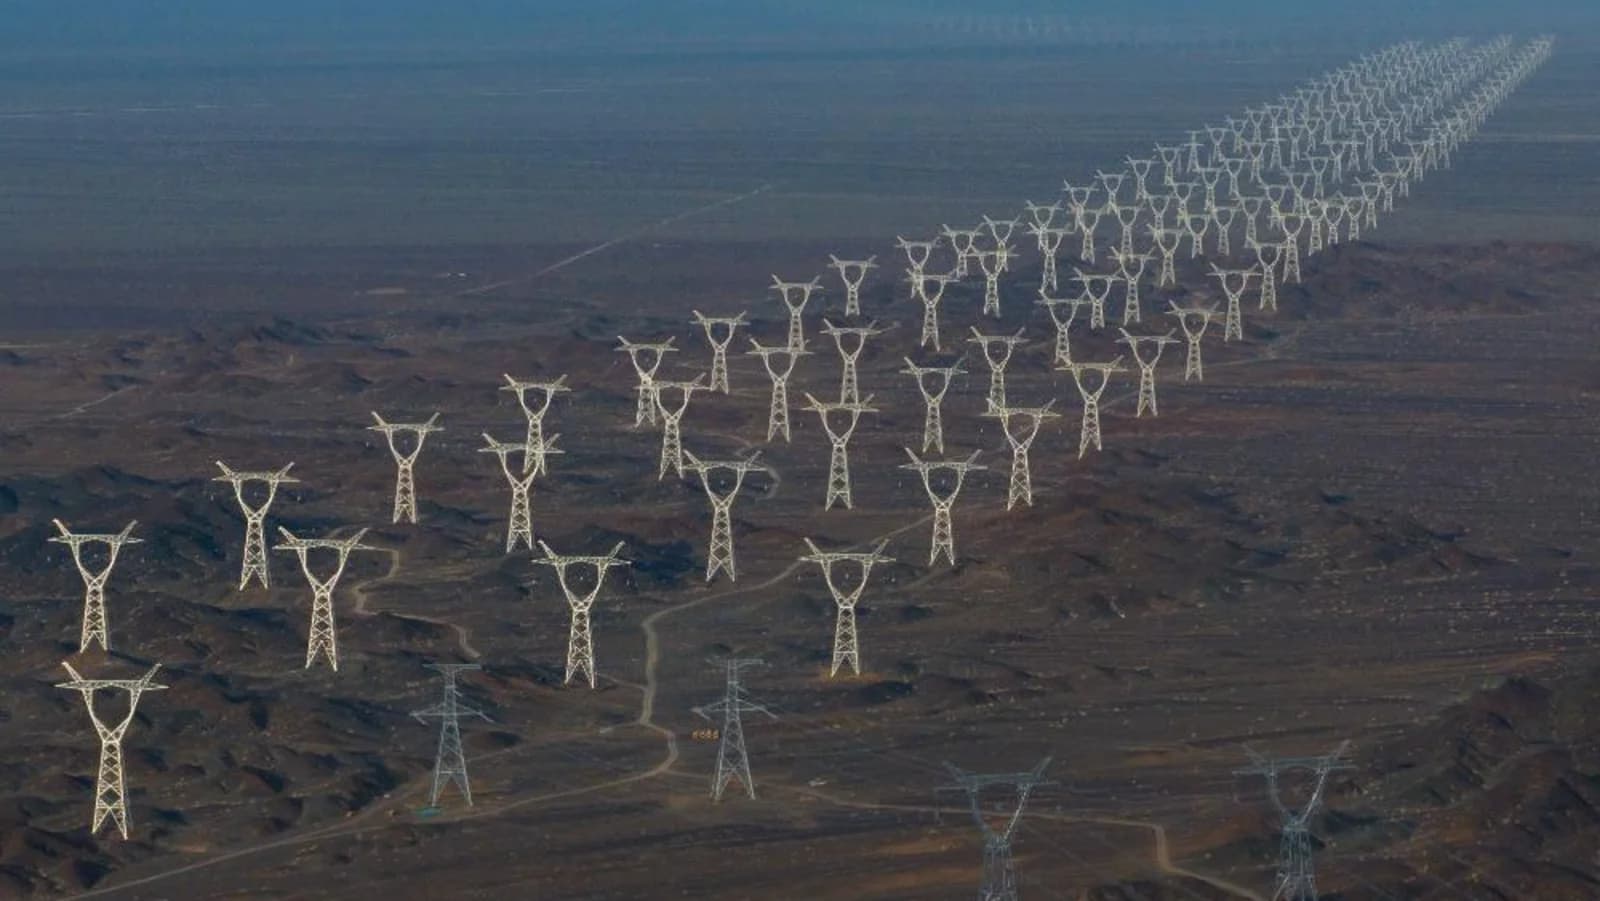 Clean energy and grid modernization
The Grid Gamble: How Electricity Could Decide the Next Industrial Superpower
China is building more than power stations and transmission lines. It is developing an electricity system designed to support AI, advanced manufacturing, electric vehicles, renewable energy, and future industries. The ambition is enormous, but so are the engineering and economic challenges.
15 min read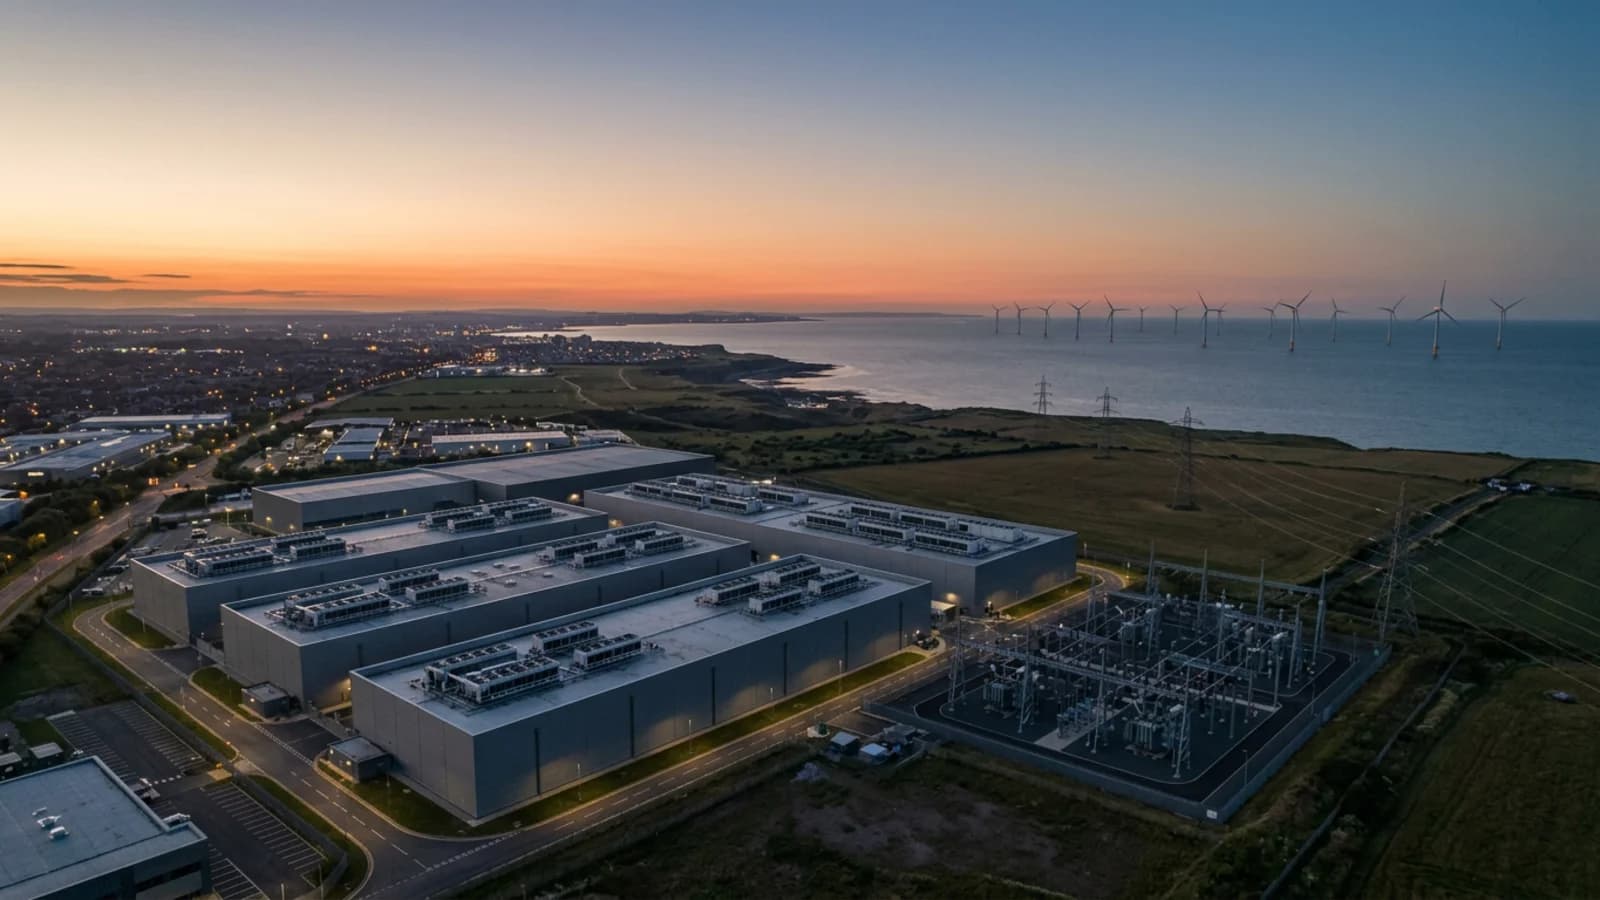 AI infrastructure
Inside the Cloud, Part 2: The AI Gold Rush Has a Plumbing Problem — and That's Just the Beginning
The expansion of artificial intelligence is creating a much larger industrial economy than most people realize. Behind the computers are energy producers, mining companies, engineers, skilled tradespeople, security specialists, and investors.
20 min read