
Got news to share with the events industry?
Submit a press release or story tip and reach thousands of event professionals.
Get in touch→More in Cybersecurity, Cryptography & Digital Trust
Krebs on Security
Attackers Used Optimizely to A/B Test Malware on Top Websites
Dark Reading
Optimizely Malware Attacks Highlight Third-Party Vendor Risks
The Hacker News
Researchers Claim Two RCE Exploits That Bypass Telegram’s New Android Defenses
The Hacker News
PHP Warns of Critical Security Flaws Affecting All Supported Versions, Fixes Coming November 19
Dark Reading
Cursor Traces Malicious Claude Code Extension to Third-Party Breach
Dark Reading
Russia's Cold Relic APT Turns One Cloud Breach Into Another
Related Insights
 Workforce transformation and the future of skills
The Time Paradox: Why Being Busy Doesn't Mean You're Moving Forward - The Foundations of Lasting Success Week 1
Busy calendars can hide stalled progress. Reclaim your attention, protect priorities, and make time for future growth.
13 min read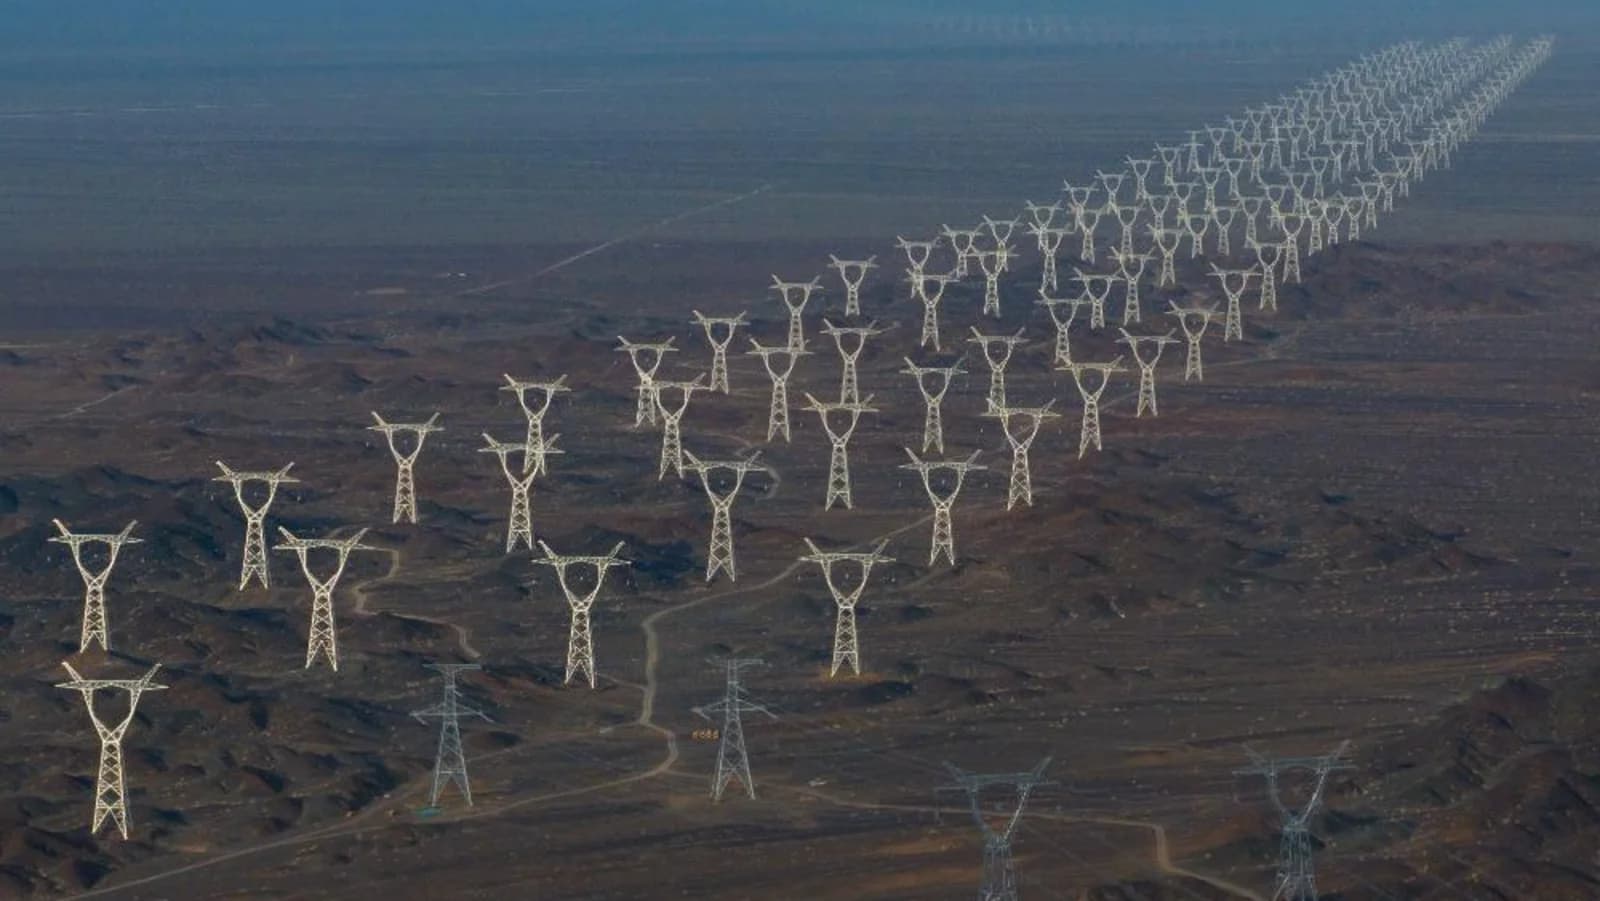 Clean energy and grid modernization
The Grid Gamble: How Electricity Could Decide the Next Industrial Superpower
China is building more than power stations and transmission lines. It is developing an electricity system designed to support AI, advanced manufacturing, electric vehicles, renewable energy, and future industries. The ambition is enormous, but so are the engineering and economic challenges.
15 min read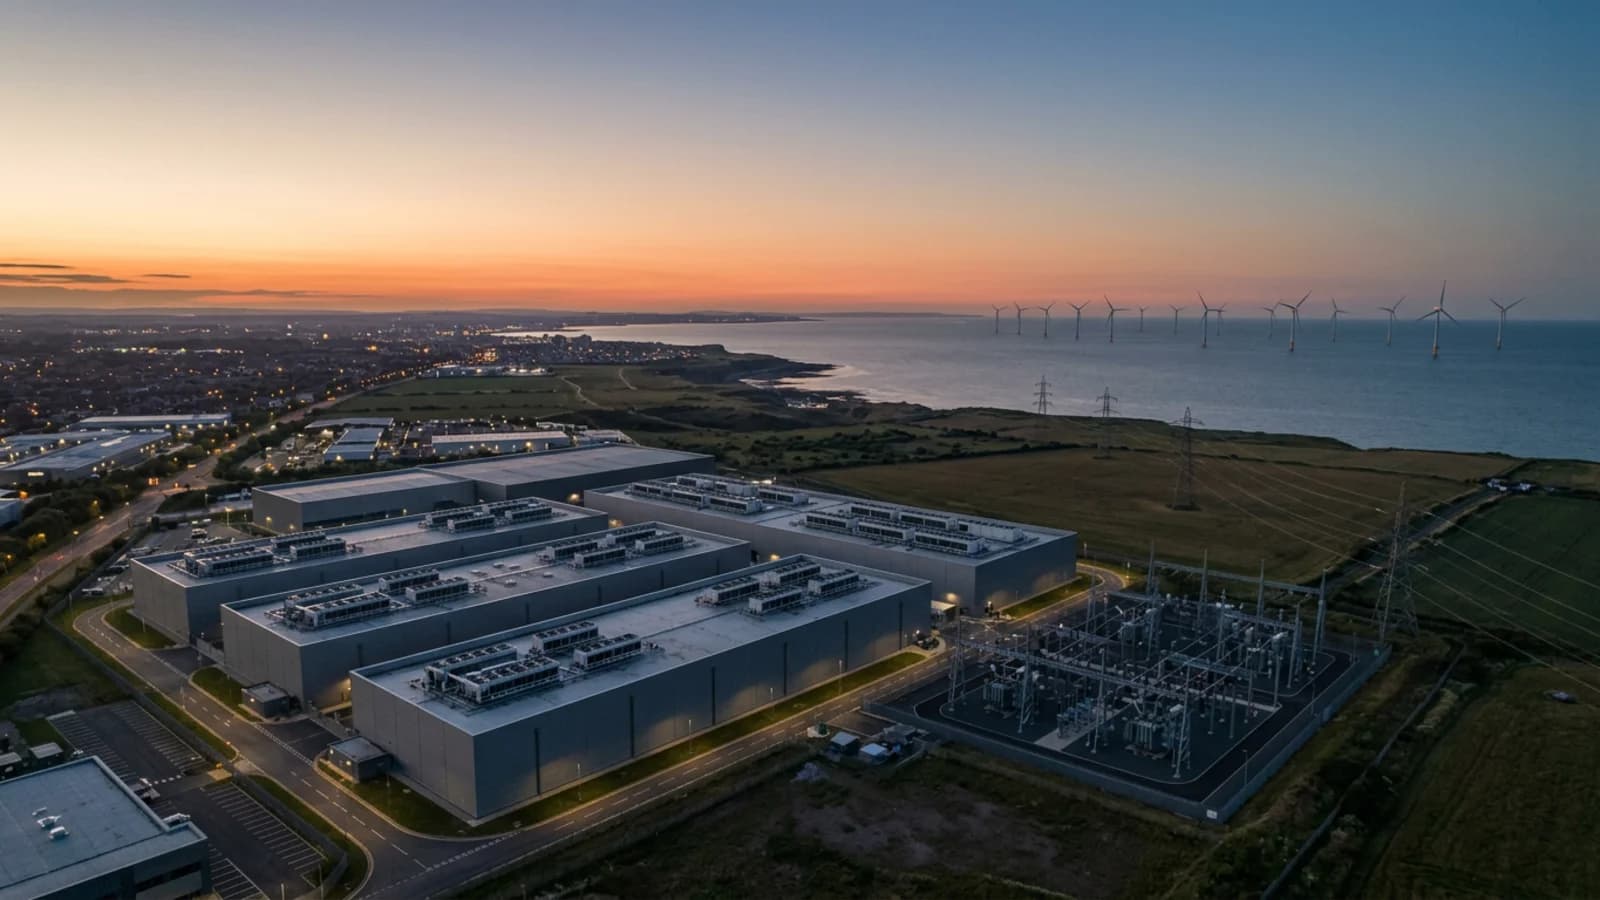 AI infrastructure
Inside the Cloud, Part 2: The AI Gold Rush Has a Plumbing Problem — and That's Just the Beginning
The expansion of artificial intelligence is creating a much larger industrial economy than most people realize. Behind the computers are energy producers, mining companies, engineers, skilled tradespeople, security specialists, and investors.
20 min read