
Got news to share with the events industry?
Submit a press release or story tip and reach thousands of event professionals.
Get in touch→More in Cybersecurity, Cryptography & Digital Trust
The Hacker News
AI-Generated Fake Login Pages Are Making Account Takeovers Easier
The Hacker News
Lazarus Abuses South Korean Security Software to Deploy Malware Using Post-Quantum Encryption
The Hacker News
Australia Gets Into Amadey Malware Backend, Cuts Off Access to 180,000 Infected Computers
Dark Reading
So Many AI Security Benchmarks, But None Tell the Whole Story
The Hacker News
OpenAI Compaction Flaw Let Researchers Bypass Hidden Reasoning Protections
The Hacker News
CISA Confirms Active Exploitation of Two PHP2Shell Flaws Enabling Remote Code Execution
Related Insights
 AI infrastructure
Inside the Cloud, Part 1: How Data Centres Are Built, Powered, Cooled and Run
Power, Cooling and 3,000 Workers: How a Data Centre Really Gets Built
20 min read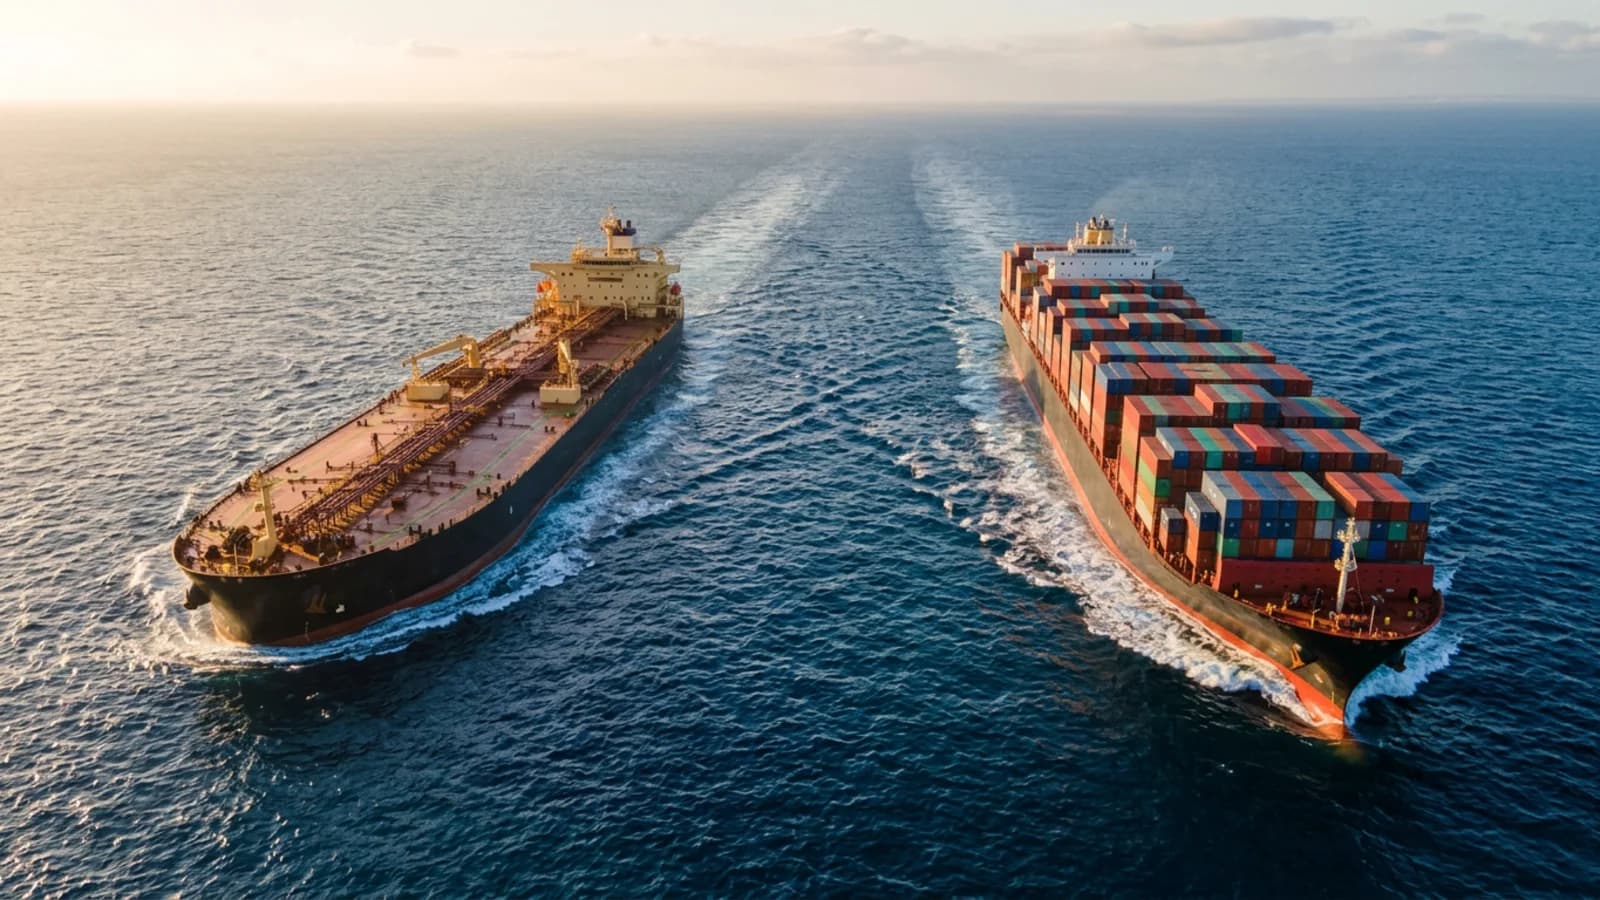 Supply chain intelligence
The Floating Economy: How Tankers and Cargo Ships Quietly Run the World
12.7 billion tonnes of goods cross the oceans a year, yet most people never see the ships. Discover how the tanker and cargo shipping business really works, who owns, builds and crews the fleet, why one strait can shake oil prices, and where the next careers and opportunities are.
24 min read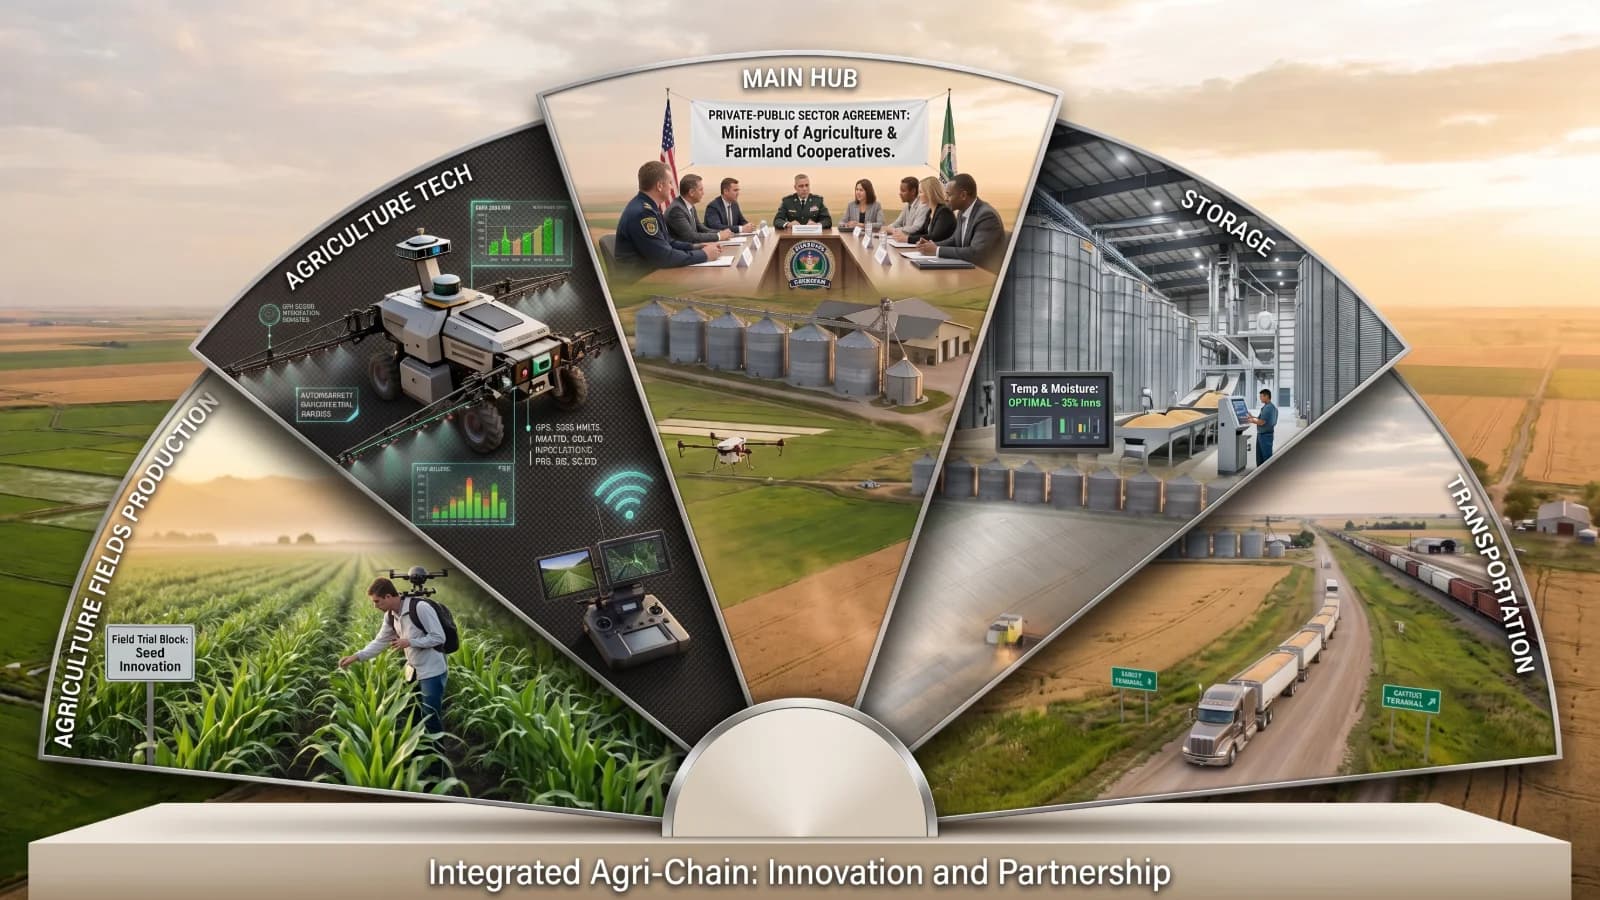 Smart agriculture and food technology
Food = Power
How China Plans to Never Run Out of Food and What the Rest of the World Can Learn
21 min read