
Got news to share with the events industry?
Submit a press release or story tip and reach thousands of event professionals.
Get in touch→More in Cybersecurity, Cryptography & Digital Trust
The Hacker News
Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware
The Hacker News
Zero Trust for AI Agents Starts With Fixing Zero Visibility
The Hacker News
SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild
The Hacker News
Bitget Says Suspected North Korean Hackers Stole $351.6M After Backend Compromise
The Hacker News
WSO2 and Adobe Commerce Flaws Exploited in Attacks, Added to CISA KEV
The Hacker News
Roundcube Pre-Auth SQL Injection Flaw Actively Exploited in the Wild
Related Insights
 Advanced manufacturing and industrial AI
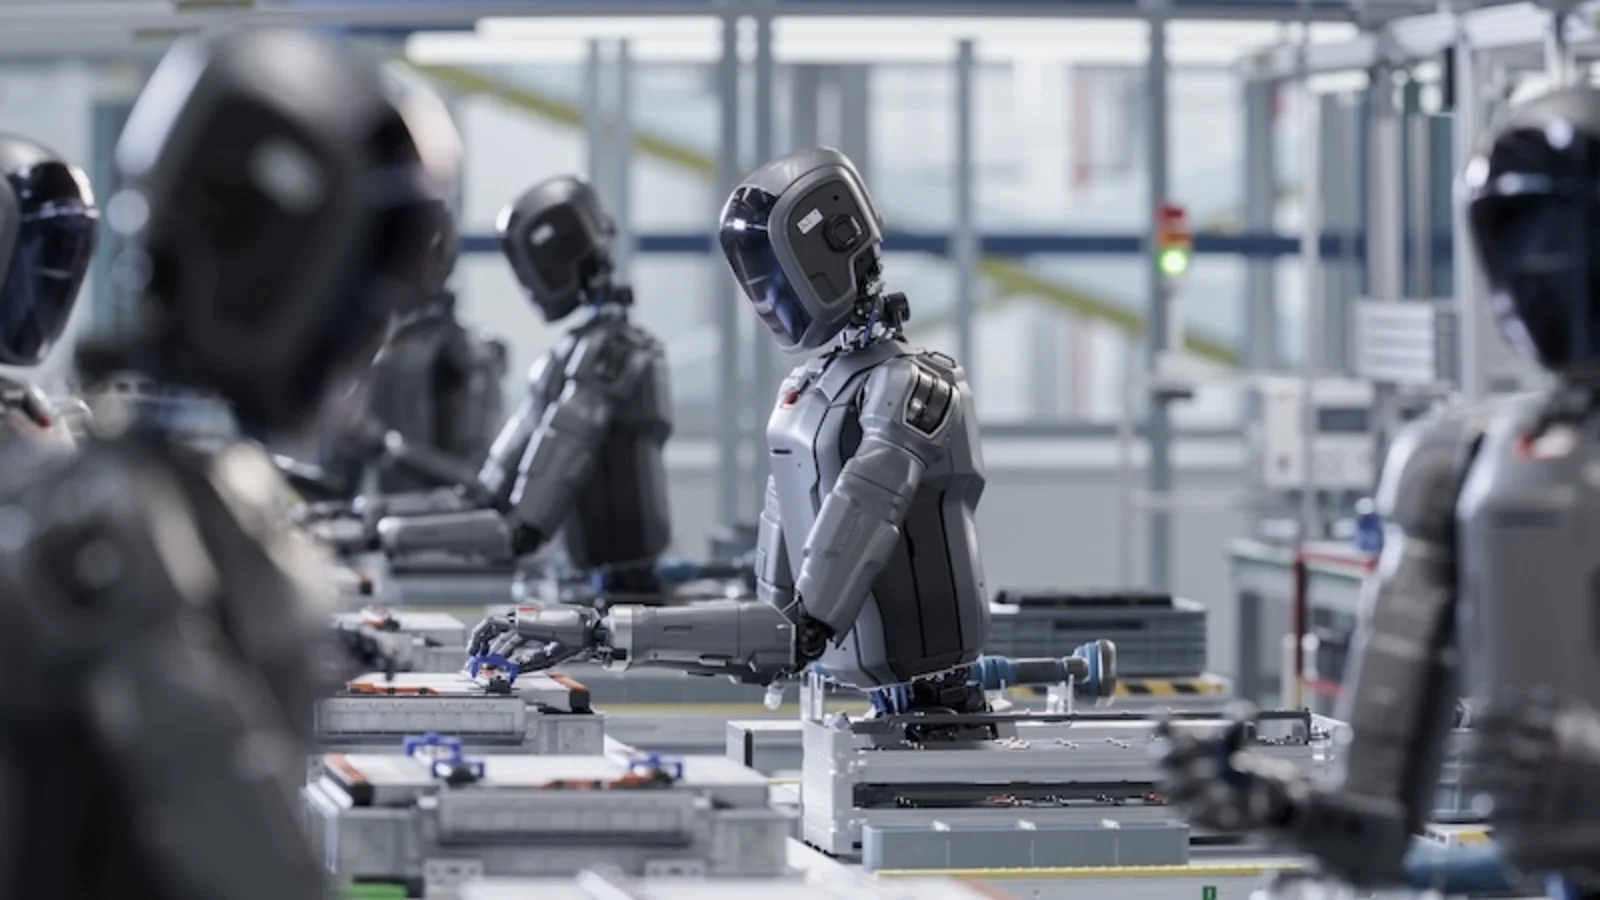
Dark Factories and Robotics
How China turned automated factories and humanoid robots into a single industrial machine — and where the opportunities are opening.
9 min read Smart agriculture and food technology
Sulfuric Acid: The Hidden Chemical Connecting Food, Metals, Clean Energy and Industrial Power
Sulfuric acid is the hidden chemical linking energy, fertiliser, food security, copper, nickel, batteries, semiconductors and water. As sulfur supply tightens, executives must track the industrial connections shaping clean technology, agriculture and global resilience.
12 min read
The Dollar System Is Being Exposed as the World’s Financial Chokepoint — and Countries Are Learning to Route Around It
The dollar still dominates global finance. But sanctions, frozen reserves, tariffs, gold repatriation, BRICS payment plans and rising geopolitical tension are forcing governments to ask a harder question: how much national security should depend on another country’s financial system?
17 min read